Vicarius
VS
Tenable
Remediation vs scanning
Vicarius was purpose-built to help security teams take action, not just generate alerts. While Tenable stops at discovery, Vicarius delivers real-time, in-platform remediation that actually fixes vulnerabilities, no external tools or delays required.

VS


















How Vicarius compares to Tenable
Capabilities
See Vicarius in action
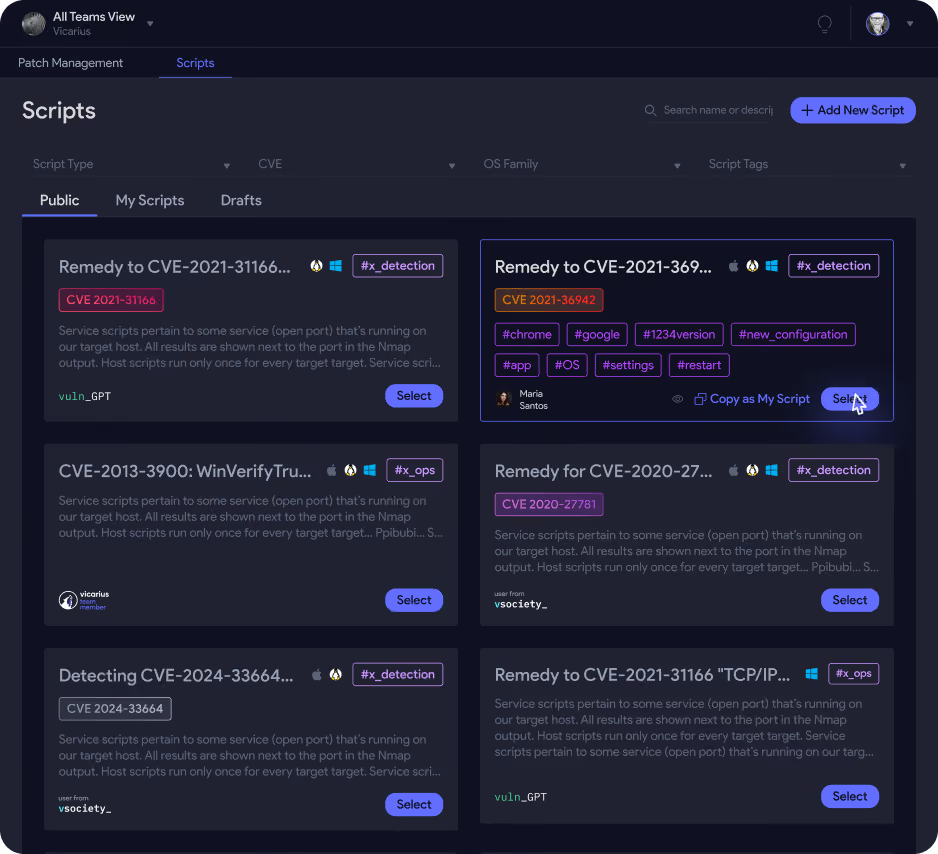
Watch how Vicarius identifies, prioritizes, and remediates vulnerabilities in real time, leveraging automation, scripts, and virtual patching. One platform to streamline remediation and take full control of your exposure.
Vicarius key differentiators


Built-in Remediation
Vicarius goes beyond detection, offering real-time, automated remediation in-platform, eliminating the operational gap Tenable leaves between scanning and patching.

Proactive Threat Mitigation
Vicarius uses AI-driven, cloud-native protection to proactively reduce risk, unlike Tenable’s reactive, scheduled scans and signature-based updates.

Low operational overhead
Vicarius provides a streamlined, modern interface with seamless deployment and centralized workflows, in contrast to Tenable’s high complexity and deployment burden.

MSSP-ready architecture
Vicarius is built for multi-tenancy and flexible pricing, while Tenable faces challenges with MSSP support and scaling across clients.

Superior Automation & coverage
Vicarius automates patching and supports over 10,000 apps with virtual patching and scripting, Tenable lacks integrated remediation and requires third-party tools.

Higher user satisfaction
Vicarius scores higher across G2 and Gartner reviews, with customers praising ease of use, patchless protection, and immediate remediation, unlike Tenable’s issues with false positives and slow scans.


Resources



4.8


4.7

Hear from our customers
From urgency to strategy
“Vicarius allowed us to step away from reactive patching and finally manage vulnerabilities with strategy instead of urgency.”

Anonymous IT Division Manager
IT Division Manager

Third-party software patching is the most valuable feature.
"We have automated third-party patching on specific software, improving efficiency by 80%. vRx has reduced our patching time, which has improved our operations. It is more robust than other solutions because it offers better third-party remediation."
Billy Turner
VP, Managed Technology & Services
Single source of truth, capable of handling any application in our fleet
"vRx gives a single pane of glass to see what patches needed to go out and what sort of vulnerabilities we have on our Windows machines. Our meantime to remediate vulnerabilities has gone down by about 60% to 70%."
Peter Fallowfield
IT Manager

Great patching capabilities, helpful dashboard, and excellent support
"vRx has saved us an incredible amount of time. We can just rely on the automated system and the schedules we've set. It's a huge time saver. It's saved us hundreds of hours."
Michael Cortez
Sr. Director of IT
Jeremy Herman
Security Engineer
Wayne Ajimine
Information Security Professional
Patchless Protection is an incredible technology!
"vRx reduces the time customers spend on patching by reducing the overhead on the administrators, allowing them to do additional work. It saves time they would spend addressing the patching process, follow-ups, etc."
Antwune Gray
VP IT Security and Services
Merge Security & IT to Remediate Threats
“Vicarius’s vRx enabled Adama to centralize and consolidate work between IT and security teams, leading to a more efficient patching workflow."
Oshri Cohen
CISO