platform

Risk-based prioritization (vScore)

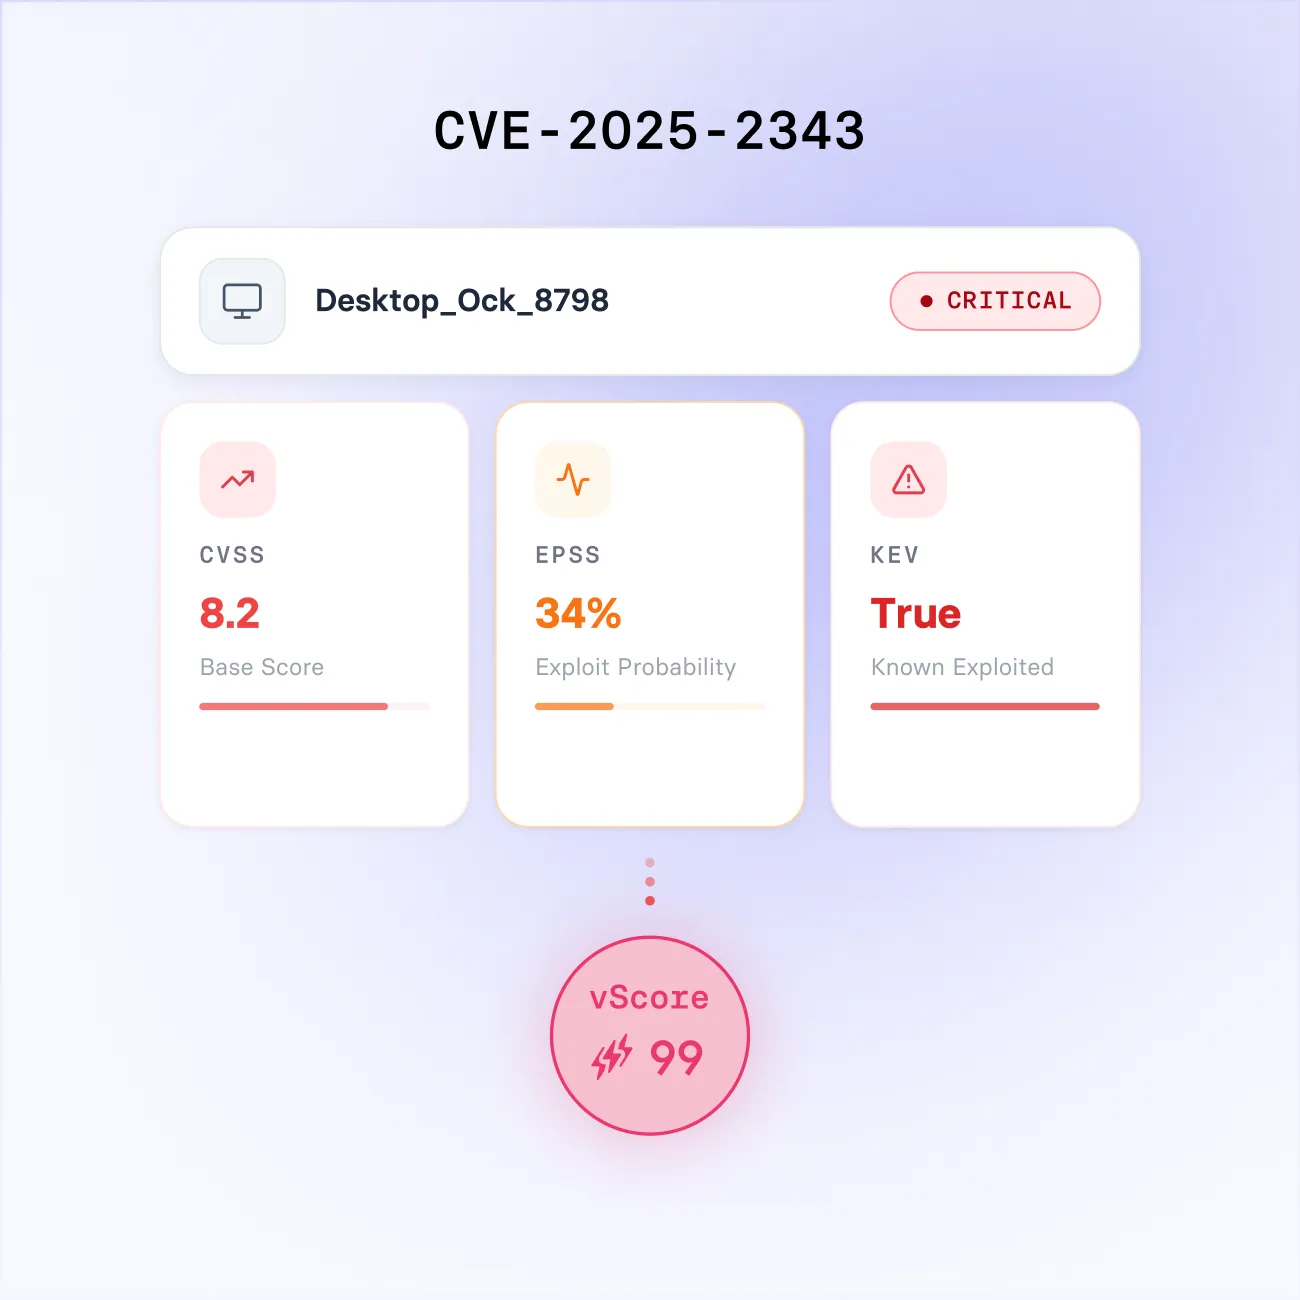
RBVM that goes beyond CVSS, EPSS, and KEV signals. vScore adds exploit simulation, asset criticality, and business context to confirm what exposes your environment and what needs fixing first.

Request a demo
95
%

fewer false positives

60
+

days average MTTR without contextual prioritization

3x

faster time from detection to remediation

benefits

Fix the right vulnerabilities every time

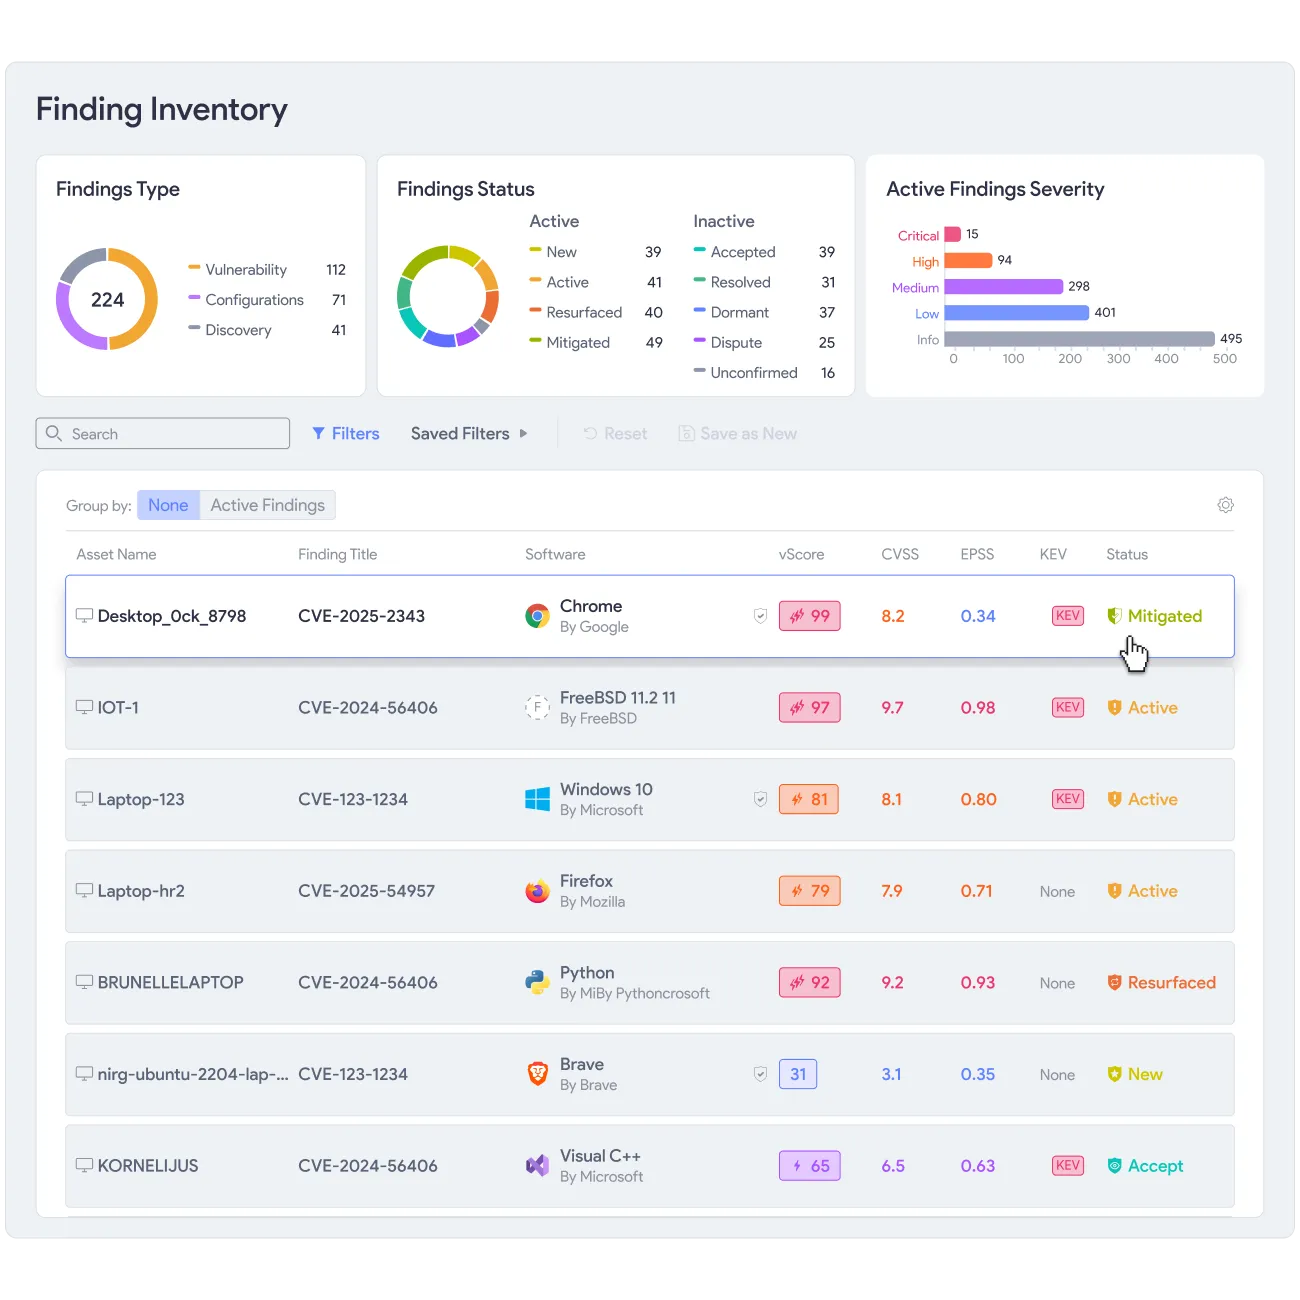
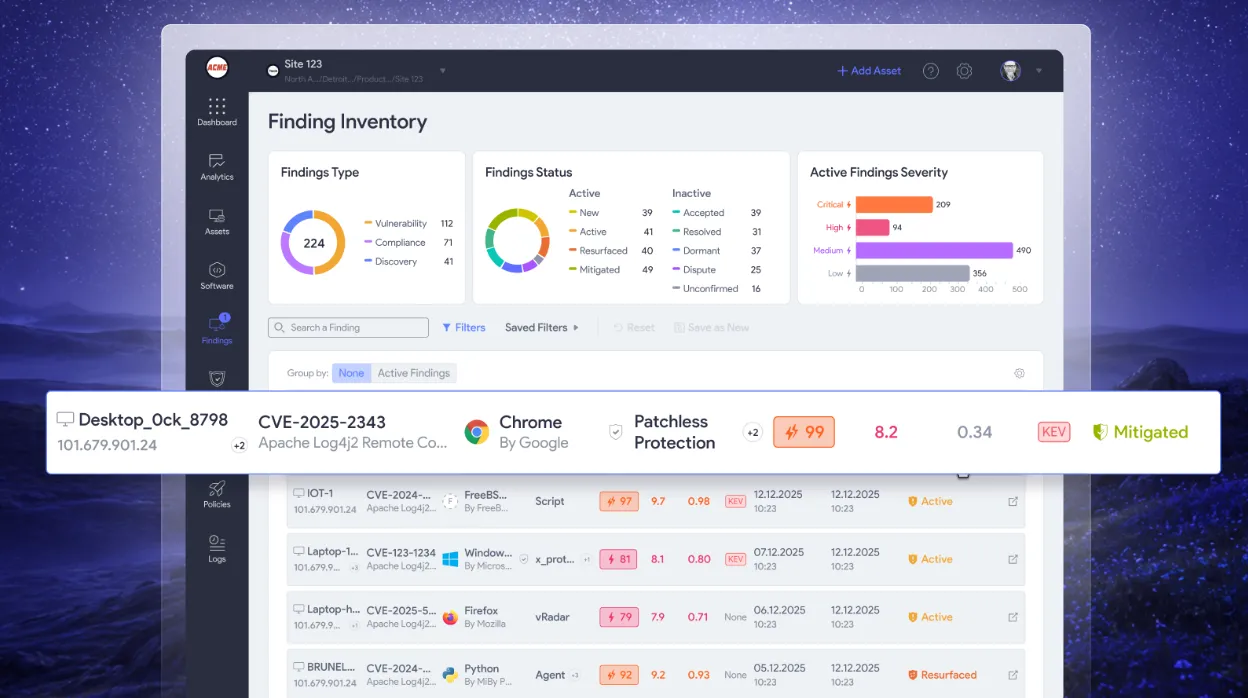
Every hour spent on the wrong vulnerability is an hour real exposure stays open. vScore delivers a ranked, validated queue so your team fixes what matters, not what looks urgent.

No false alarms

vScore confirms every queued item is exploitable. Your team works on real threats, not false alarms.

Your risk, ranked

Your priority list reflects your environment, not generic CVE scores. vScore factors in your asset criticality and business context.

95% less noise

Your team stops investigating alerts that go nowhere. Agentic Exposure Validation cuts 95% of false positives before they reach you.

No tool switching

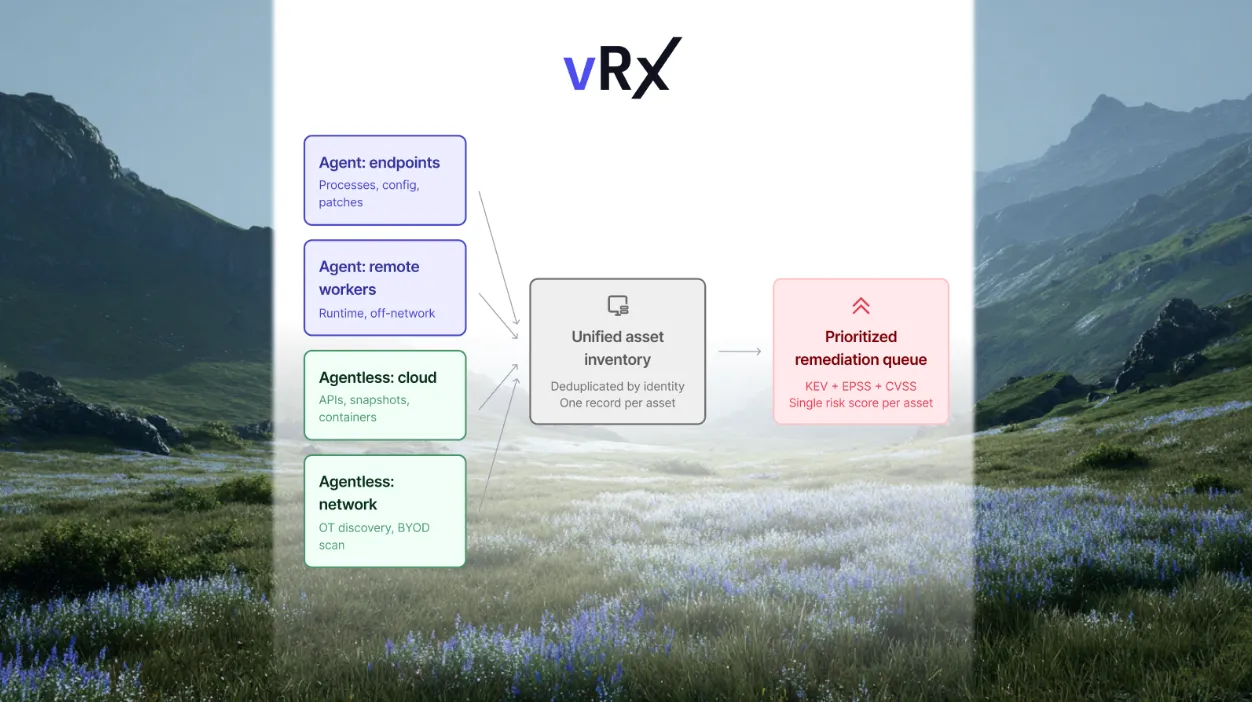
Your EDR, SIEM, CSPM, and scanners all feed one ranked list. One source, not four to reconcile.

No manual triage

Your team gets a ranked, validated queue, ready to fix. Time goes to remediation, not research.

Know it worked

After every fix, you confirm the risk went down. vScore re-validates every asset automatically, leaving nothing assumed done.
key capabilities

How vScore ranks real risk

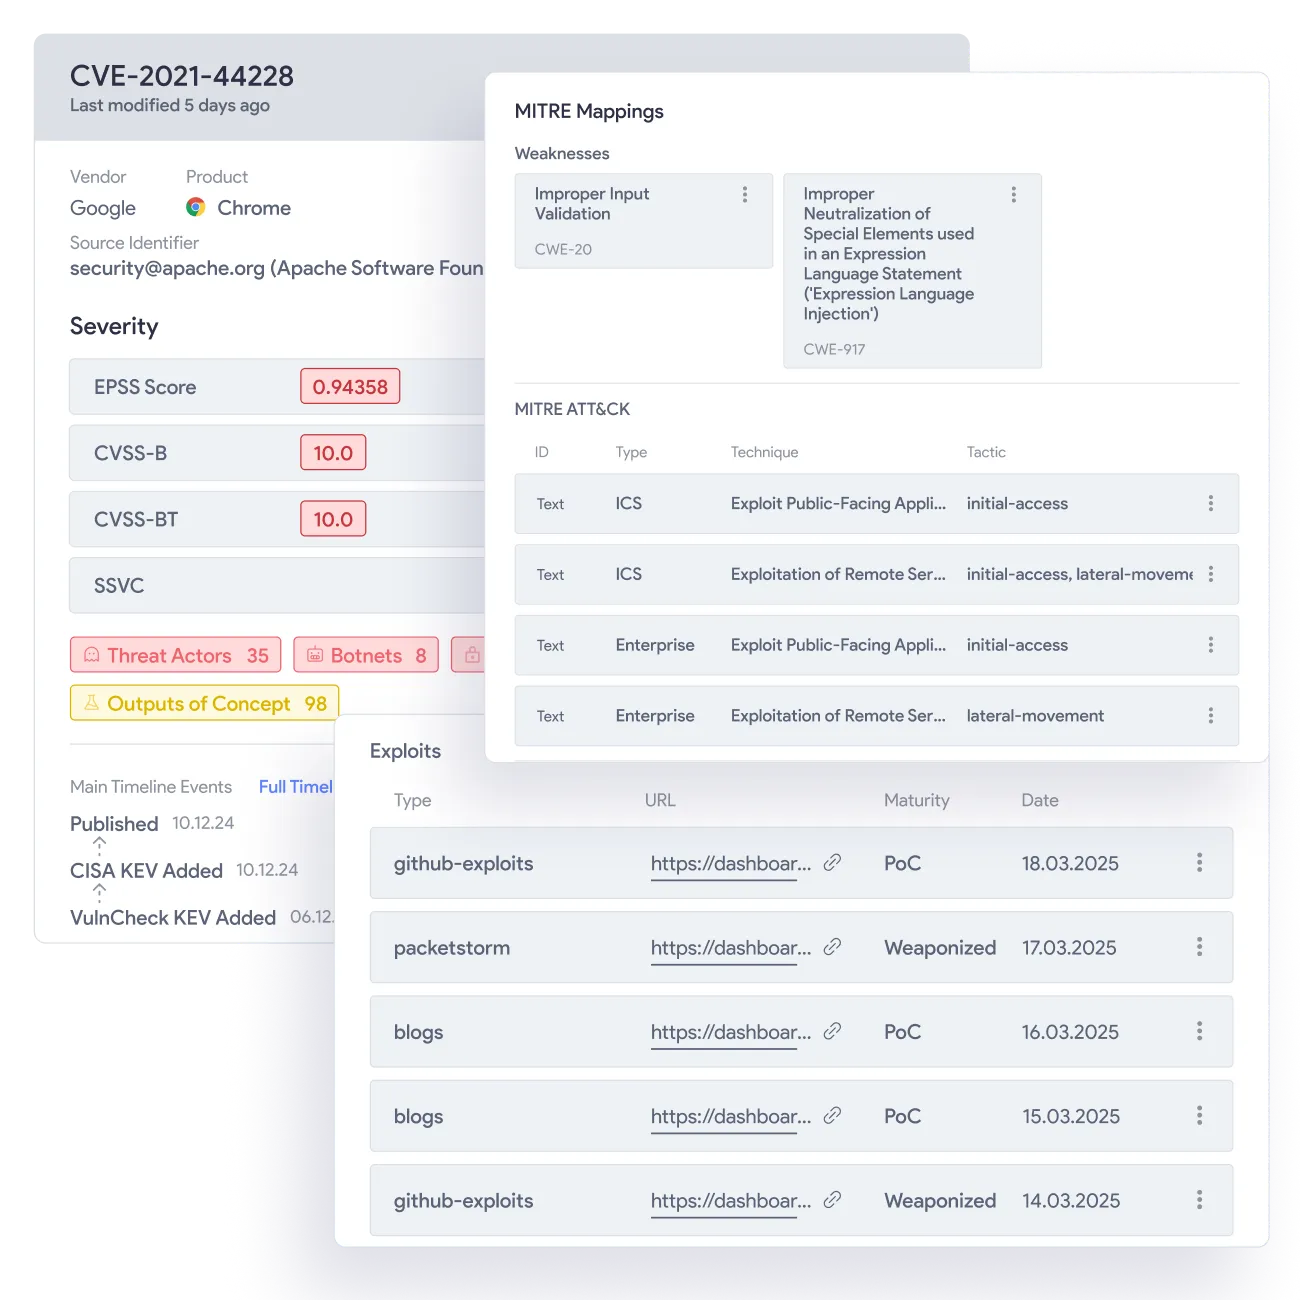
vScore ingests CVSS, EPSS, and KEV signals alongside exploit simulation, weaponization intelligence, asset context, and business criticality to produce a single risk score for every CVE. The result is a prioritized queue your team acts on immediately.

Resources

Additional Resources

Read article

Why agentless + agent-based scanning together create a complete risk picture

Read article

A deep dive Into risk score calculation: how vRx by Vicarius prioritizes what matters

Read article

CVSS vs EPSS vs KEV which score actually matters?

Shortlist 2024 by Captera
Tech leader award by PeerSpot
4.8
Customer first by Gartner
4.7
Customer first by Gartner
Leader spring by G2
Leader spring by G2
Leader spring by G2
Leader spring by G2

What Our Customers Say About Us

See why enterprises trust our approach to AppSec to secure their business-critical applications

All in one platform

We chose Vicarius vRx for efficient third-party software patching, as Microsoft's solutions fall short. Though challenging for servers, it's effective for end-user devices. We value its patching ability but desire a cloud testing environment. We've considered alternatives, but vRx excels in support.
Michael Sutherland
Michael Sutherland
IT Security Manager at Jamaica Broilers Group

From urgency to strategy

“Vicarius allowed us to step away from reactive patching and finally manage vulnerabilities with strategy instead of urgency.”
Anonymous IT Division Manager
IT Division Manager

EL AL secures global Patch Compliance

“Within two weeks we decided on Vicarius. Patch scheduling is now a one-day task instead of a full-time job.”
Tal Shachar
Tal Shachar
Deputy Director, Infrastructure, EL AL Airlines

Complete Vulnerability Remediation Platform

"What stood out was that it wasn’t just a scanner or a patch manager. It was an entire remediation platform. You discover vulnerabilities, prioritize based on real risk, and remediate automatically."
Eric Dowsland
Eric Dowsland
Chief Customer Officer

Não espere até que o WSUS seja completamente descontinuado. Agende uma demonstração e descubra como o vRx pode transformar sua estratégia de gerenciamento de patches.
Billy Turner
Billy Turner
VP de Tecnologia e Serviços Gerenciados​

Excelente capacidad de parcheo, un panel útil y soporte excepcional

Rvx nos ha ahorrado una cantidad increíble de tiempo. Ahora podemos confiar completamente en el sistema automatizado y en los horarios establecidos. Nos ha ahorrado cientos de horas.
Michael Cortez
Michael Cortez
Director de IT Senior

Hervorragende Patch-Fähigkeiten, ein hilfreiches Dashboard und exzellenter Support

Rvx hat uns unglaublich viel Zeit gespart. Wir können uns einfach auf das automatisierte System und die von uns festgelegten Zeitpläne verlassen. Es spart uns enorm viel Zeit. Es hat uns hunderte Stunden eingespart.
Michael Cortez
Michael Cortez
Senior IT-Direktor

Excellentes capacités de mise à jour, tableau de bord pratique et support exceptionnel

« Rvx nous a fait gagner un temps considérable. Nous pouvons simplement nous fier au système automatisé et aux plannings que nous avons définis. C’est un énorme gain de temps. Nous avons économisé des centaines d’heures. »
Michael Cortez
Michael Cortez
Directeur(trice) principal(e) de l’informatique

Valuable resources saved

"Before vRx, we would spend countless hours manually finding and verifying patches. We saved so much time (and headache!)."
Anonymous IT Operations Lead
IT Operations Lead

Third-party software patching is the most valuable feature.

"We have automated third-party patching on specific software, improving efficiency by 80%. vRx has reduced our patching time, which has improved our operations. It is more robust than other solutions because it offers better third-party remediation."
Billy Turner
Billy Turner
VP, Managed Technology & Services

Single source of truth, capable of handling any application in our fleet

"vRx gives a single pane of glass to see what patches needed to go out and what sort of vulnerabilities we have on our Windows machines. Our meantime to remediate vulnerabilities has gone down by about 60% to 70%."
Peter Fallowfield
Peter Fallowfield
IT Manager

60% faster remediation, many hours saved

"Typically, with our previous solution of ManageEngine, it took about three hours to patch Windows Server, and now, that is less than an hour. It means less downtime for the business each month when we do patches."
Anonymous Security Analyst
Security Analyst

Great patching capabilities, helpful dashboard, and excellent support

"vRx has saved us an incredible amount of time. We can just rely on the automated system and the schedules we've set. It's a huge time saver. It's saved us hundreds of hours."
Michael Cortez
Michael Cortez
Sr. Director of IT

My favorite feature is Patchless Protection

"With Vicarius' vRx, I've never seen a patch that failed or had to be rolled back. We're saving quite a bit of time. Our clients using vRx haven't had any issues, and they've easily established patching for all their endpoints."
Jeremy Herman
Jeremy Herman
Security Engineer

Unified vulnerability discovery, prioritization, and remediation

"Vicarius streamlines vulnerability management between IT & Security by directly linking identified vulnerabilities to required patches, enhancing efficiency. The automation process has saved at least 30 percent of our manual tasks."
Wayne Ajimine
Wayne Ajimine
Information Security Professional

Patchless Protection is an incredible technology!

"vRx reduces the time customers spend on patching by reducing the overhead on the administrators, allowing them to do additional work. It saves time they would spend addressing the patching process, follow-ups, etc."
Antwune Gray
Antwune Gray
VP IT Security and Services

Merge Security & IT to Remediate Threats

“Vicarius’s vRx enabled Adama to centralize and consolidate work between IT and security teams, leading to a more efficient patching workflow."
Oshri Cohen
Oshri Cohen
CISO

Everything you need to know

HeadingWhat is RBVM and how does Vicarius approach it?

RBVM, or Risk-Based Vulnerability Management, is the practice of prioritizing vulnerabilities based on real business risk rather than theoretical severity alone. Vicarius implements RBVM through vScore, combining CVSS, EPSS, and KEV signals with exploit simulation, asset criticality, and business context into a single prioritized remediation queue.
Why are CVSS, EPSS, and KEV not enough on their own?

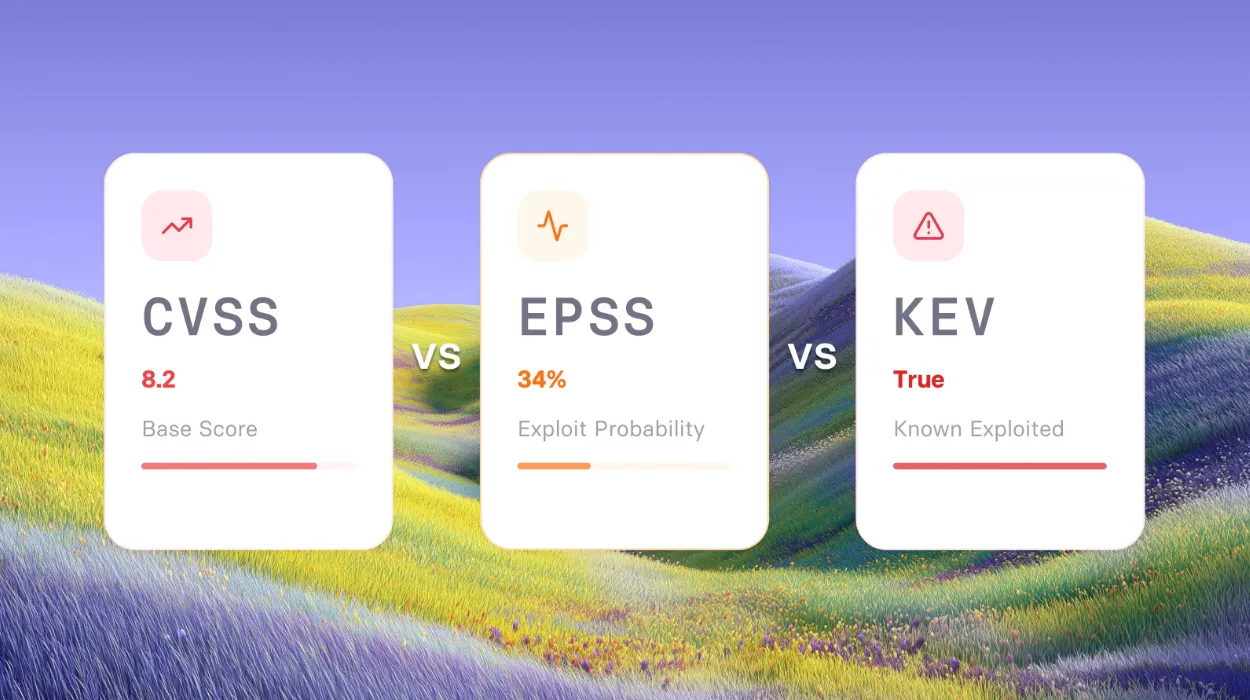
CVSS rates theoretical severity. EPSS predicts exploit probability. KEV confirms active exploitation. Together they narrow the field, but none account for your specific environment, asset value, or business impact. vScore takes all three as inputs and adds the contextual layer that turns signals into a ranked, actionable queue.

What is vScore and how does it work?

vScore is Vicarius's RBVM scoring engine. It ingests CVSS, EPSS, and KEV data alongside exploit simulation results, asset criticality, and business context to produce a single risk score that reflects each vulnerability's real threat in your specific environment.

How does Agentic Exposure Validation reduce false positives?

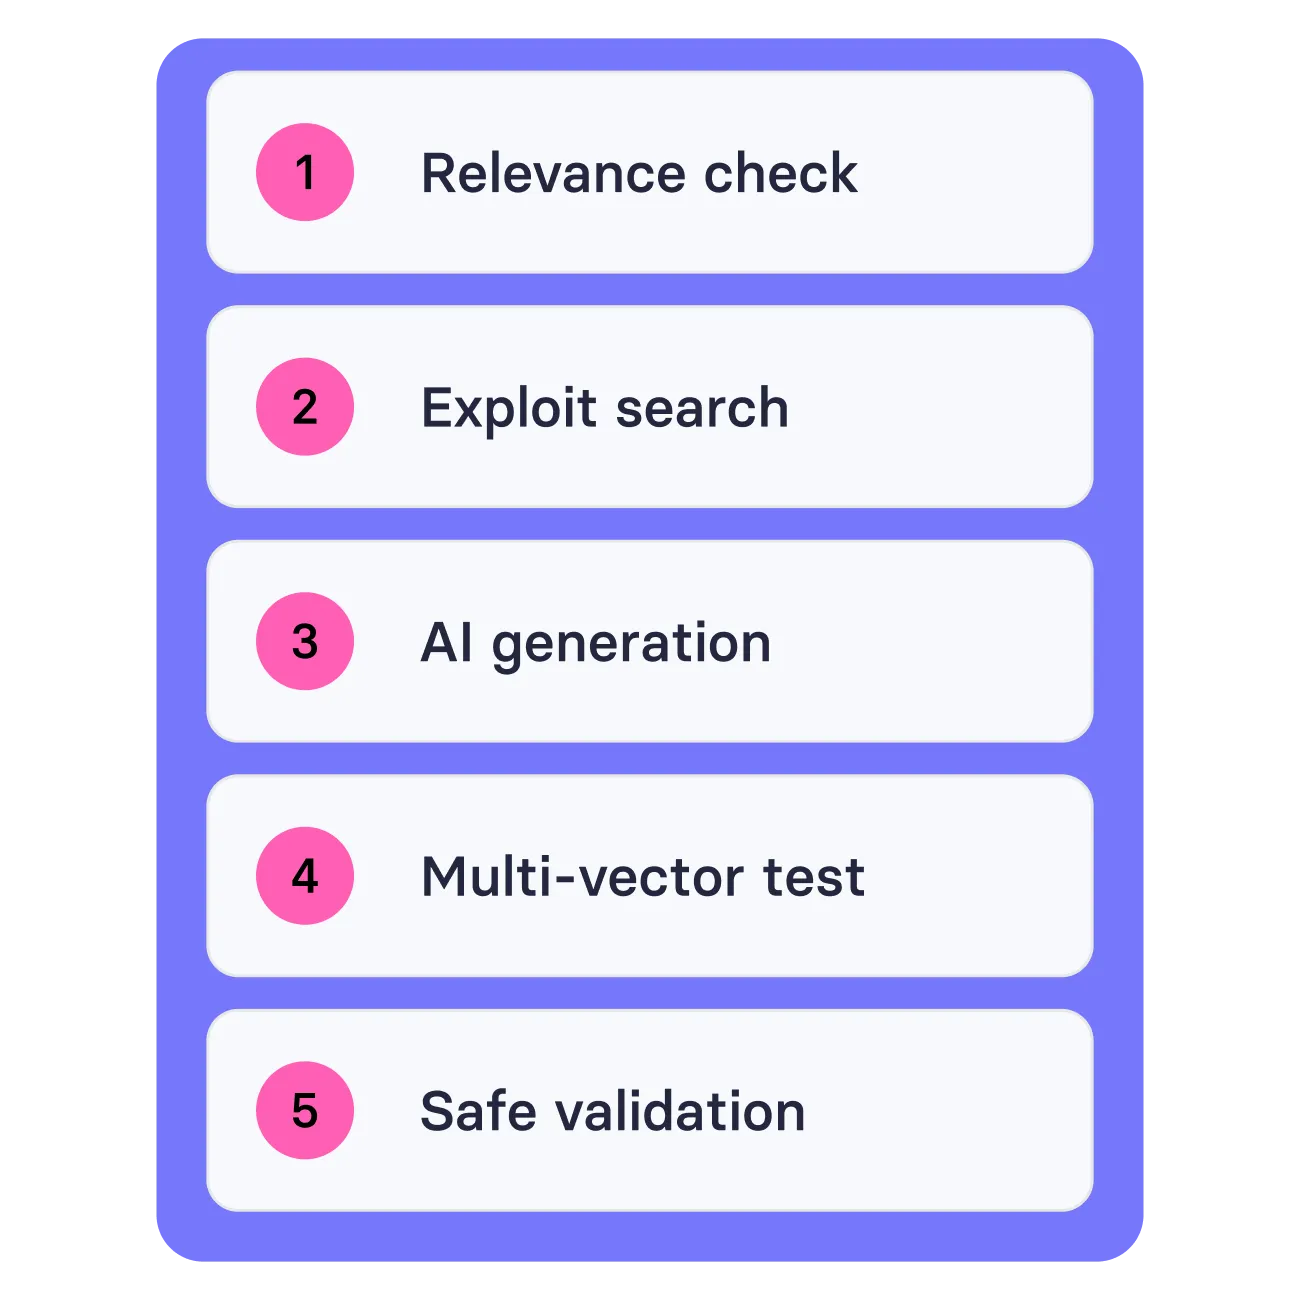
vIntelligence runs exploit simulations against your live environment to test each vulnerability, confirming what is genuinely exploitable versus what is theoretical. This cuts 95% of false positives before they reach your remediation queue.
How does risk-based prioritization connect to remediation?

Once vScore ranks your vulnerabilities, vRx delivers a fix path for every one using automated patching, patchless protection, or AI-generated scripts. Re-validation then confirms each remediation reduced or removed the risk.
Can vScore work alongside my existing vulnerability scanner?

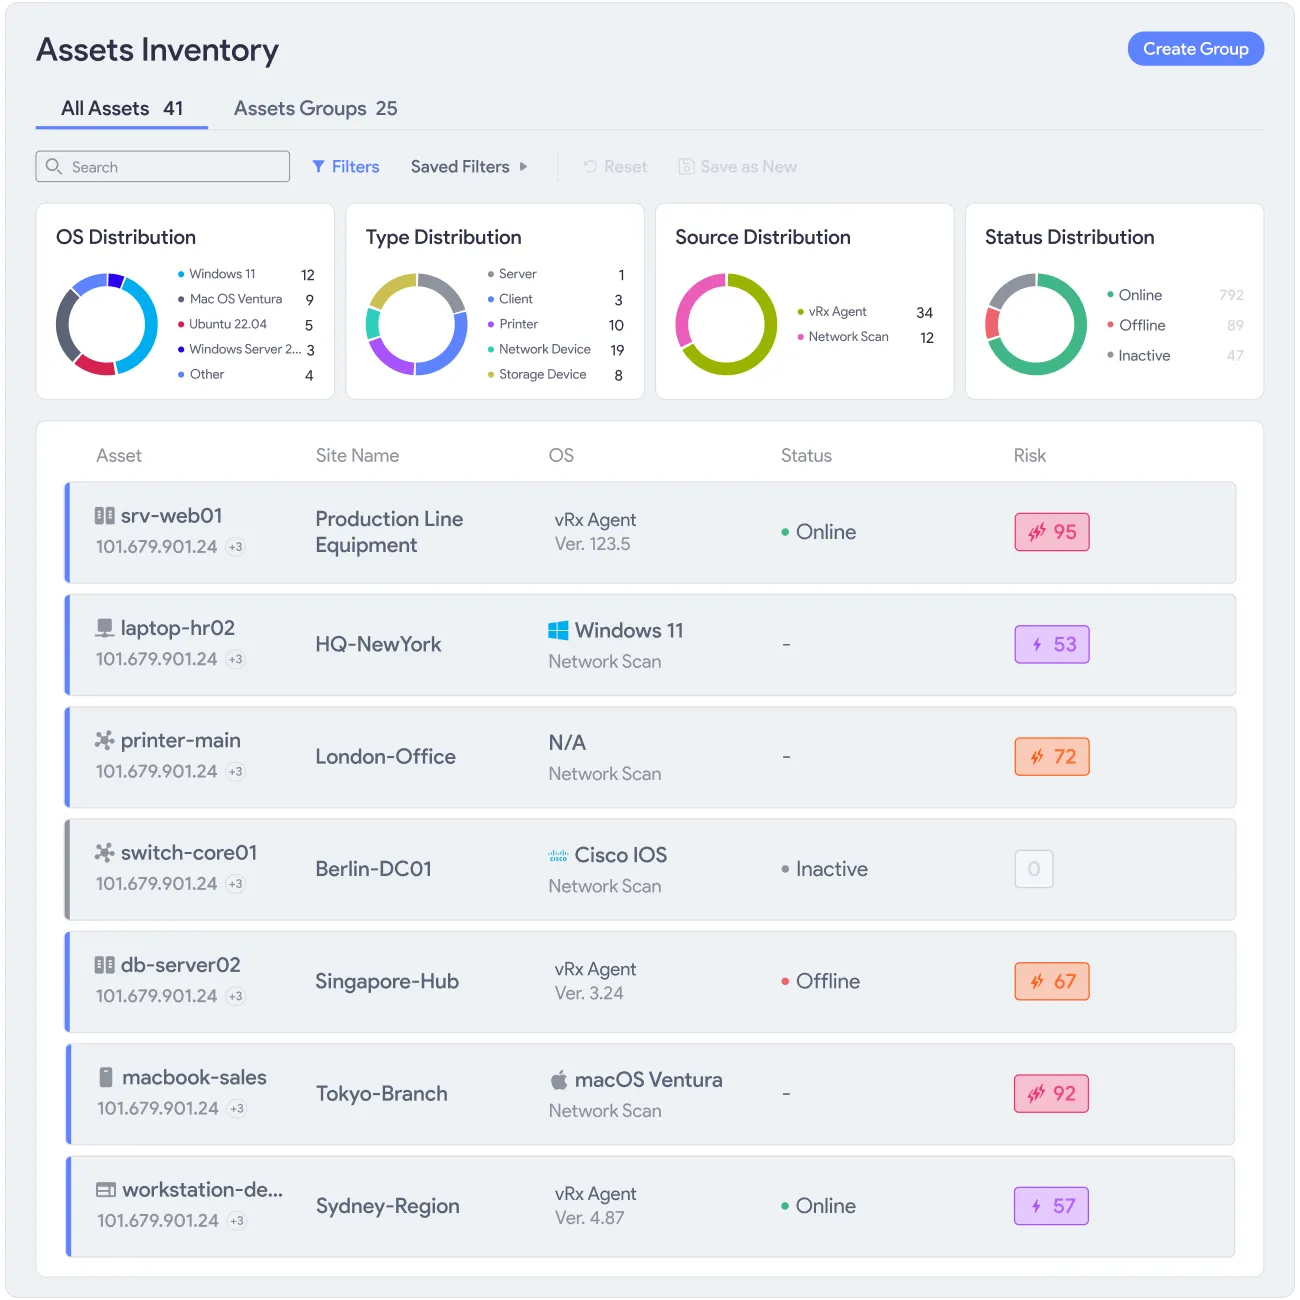
Yes. vIntelligence ingests findings from your existing scanners alongside signals from your EDR, SIEM, CMDB, and CSPM, normalizing them into a unified queue scored by vScore.

How does risk-based prioritization reduce analyst workload?
vScore delivers a validated, ranked queue that eliminates hours of manual CVE research, correlation, and triage. Your team works from one prioritized list instead of reconciling output from multiple disconnected tools.

4.7/5

Remediate more vulns with vRx