1. Understanding How Apple Provisioning Works
While provisioning a Mac is not really complex, the process is different from the traditional imaging method. More importantly, Apple provisioning is done through the Device Enrollment Program, which runs in the cloud and can be accessed through the Apple Business Manager Application.
After registering device serial numbers in the device enrollment program (DEP), IT will register the devices in a mobile device management (MDM) tool. The tool helps IT to set up group policy objects (GPO). This includes settings for the configuration of users based on their designated user group.
Additionally, it shows the applications that users should see on their desktop and their security access settings. Most times, this procedure looks strange to IT administrators who have only worked in Windows environments.
The most essential Mac patching process is that the MDM installs the settings and applications to the devices through the Apple cloud. Therefore, end users can start working without IT professionals ever having to physically touch their Mac during the provisioning process.
2. Deliver Updates to Mac Efficiently
The procedure for applying OS updates and security patches for Mac is simplified with a free service from Apple which is called MacOS updates. For Mac, it’s ideal to test different configurations to ensure patches and updates won’t break any applications and operating systems in the environment.
The specific services to test include the ability to log into email, utilize VPN services and access files in shared drives. It’s important to test when deploying antivirus software because it can break the operating system and cause machines to crash.
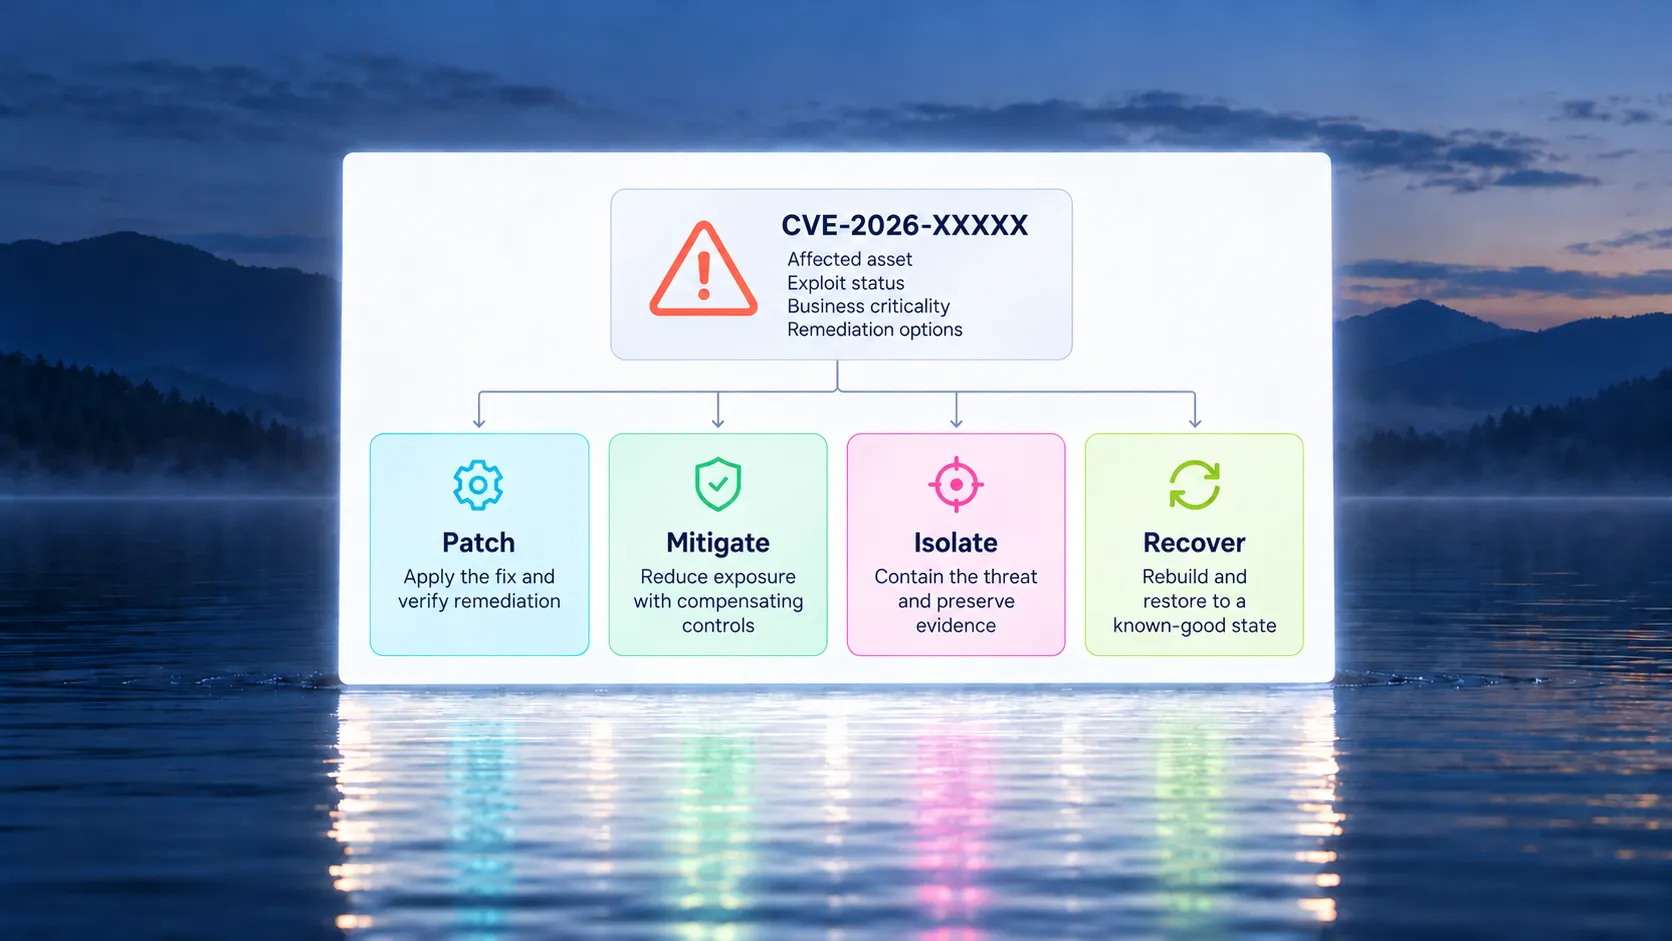
Manage macOS updates through a supported device-management service rather than building a new workflow around the discontinued macOS Server product. Define the approved update, deployment population and installation deadline, then confirm the resulting device state. Keep macOS updates and third-party application updates as separate parts of the patching plan: their distribution methods and verification requirements are not interchangeable.
3. Secure Mac with Authentication Measures
The major way to ensure Mac security is two-factor authentication. In addition to using usernames and passwords, IT professionals can request a unique code that is sent via a text message which they need to enter before getting access to the system. Alternatively, IT administrators can give users a thumb drive to plug into their devices. Without the unique code or thumb drive, users won’t be able to log in to their system.
For user identity services, Active Directory is the major tool that IT teams are familiar with. However, Macs can have performance issues when connected directly to it. In order to simplify the process, IT professionals can use tools like Apple Enterprise Connect and Jamf Connected to eliminate the need for local machines connected directly to Active Directory, while also tracking account credentials on local machines.
Set authentication requirements according to the organization’s risk assessment and applicable obligations. Set authentication requirements according to your organization’s risk assessment and applicable obligations. NIST’s digital identity guidance recommends against requiring periodic password changes without evidence of compromise. The easier it is for users to get technical support, the easier it will be for IT to deploy and administer Mac security updates.
The initial step is to ensure that your Mac device users know who to contact when issues occur. This will ensure users can get the assistance they need effectively and efficiently, reducing the threats or vulnerabilities and speeding the patching process.
Self-service applications can reduce support desk phone calls and tickets. This is due to users having access to already approved and safe applications whenever they need them. Furthermore, the ability to run maintenance tasks to fix minor issues will also help users feel empowered and ensure little issues get fixed immediately, instead of waiting in the IT queue.
Are You Ready for Mac Best Practices?
For IT administrators, especially those without previous experience, initial deployment may seem complex, but with the above Mac patching practices and the business tools offered by Apple, your users can be up and running immediately.
Vicarius is a vulnerability remediation tool that targets cybersecurity officers as well IT managers and operators from the U.S. market. Our products and services are personalized to your unique business and always incorporate Mac best practices.
Related resources: