Last updated: October 2026
Qualys vs Tenable: the quick verdict
Choose Tenable if you want the deepest vulnerability scanning, an on-prem option and published pricing. Choose Qualys if you want scanning and remediation from one vendor in one cloud platform, and you're prepared to pay for the remediation modules. Both are excellent at finding vulnerabilities. Neither includes patching in its core vulnerability management licence.
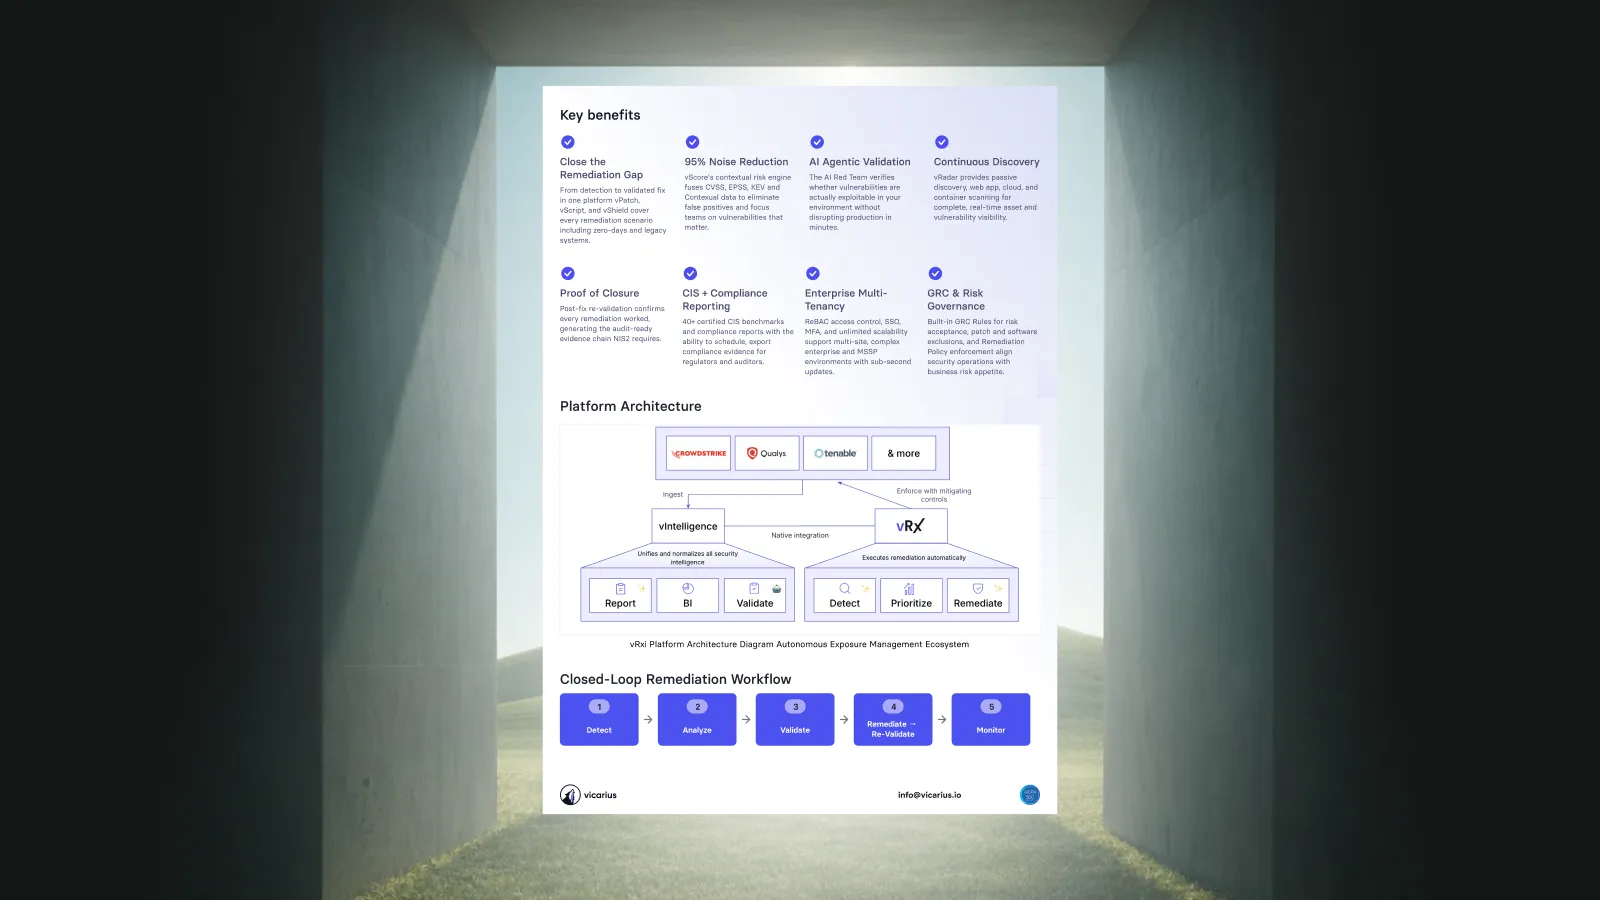
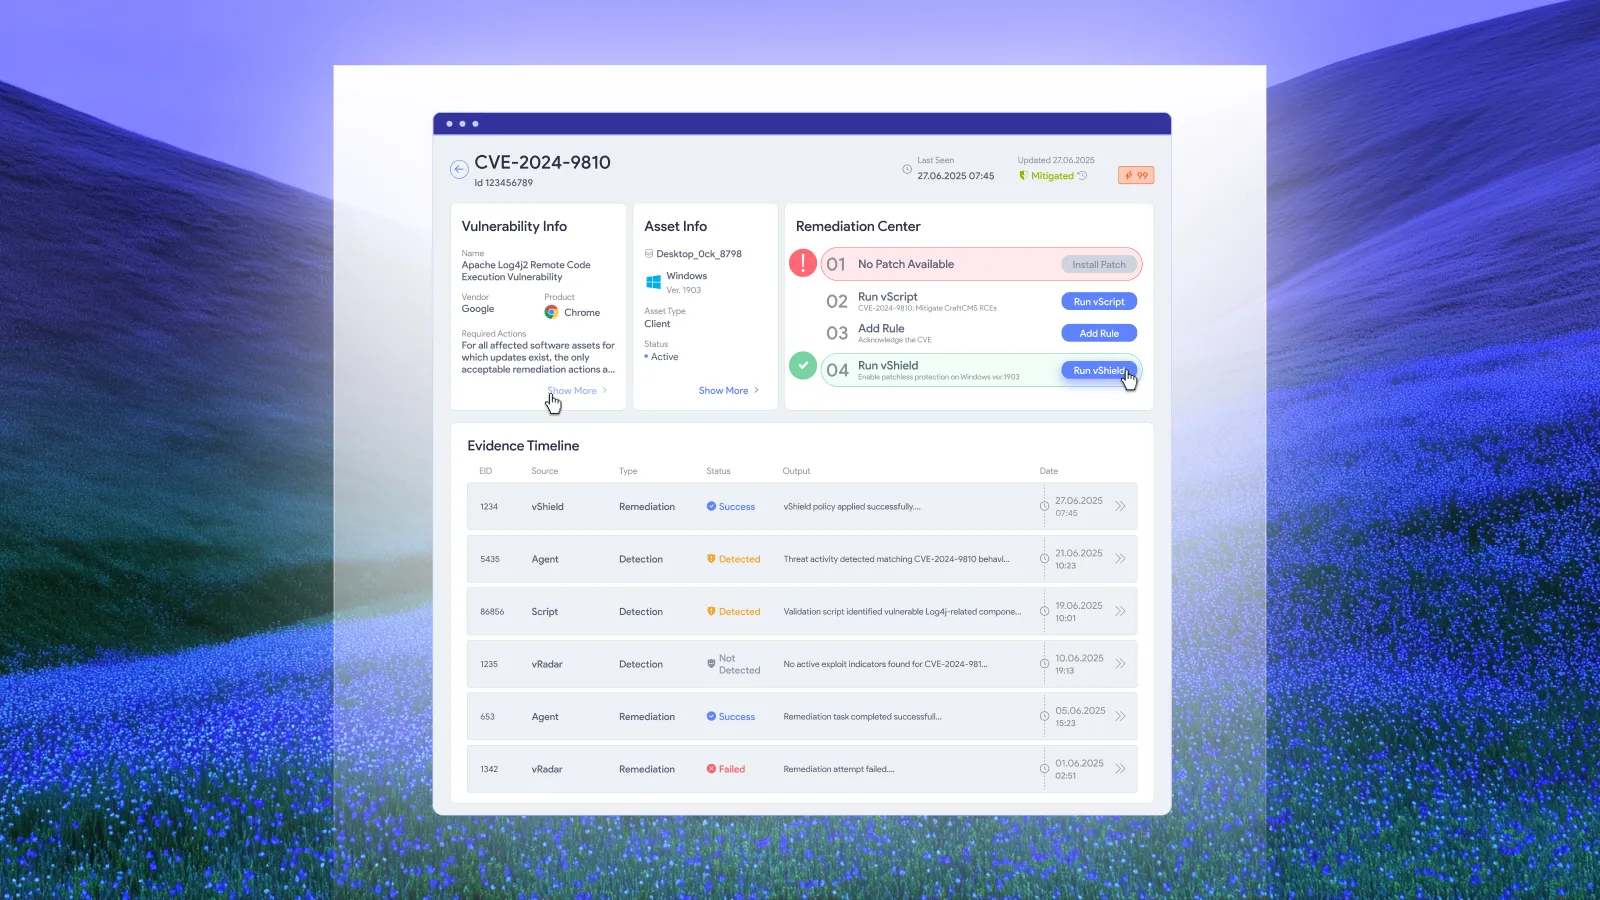
If your real bottleneck is fixing, not finding, a remediation-first platform such as Vicarius vRx includes patching, scripted fixes and patchless protection natively, rather than as add-ons.
Disclosure: Vicarius makes vRx, a vulnerability remediation platform. We've aimed to be fair to both Qualys and Tenable.
Qualys and Tenable in 2026: what each sells
Both vendors have grown from scanners into broad exposure management platforms, and the product names have changed along the way. That's why many older comparisons, including earlier versions of this one, still refer to "http://Tenable.io " and "http://Tenable.sc ".
Qualys
- VMDR (Vulnerability Management, Detection and Response): the core vulnerability management product. It runs in the Qualys cloud and uses the Qualys Cloud Agent and network scanners.
- Patch Management and TruRisk Eliminate: Qualys's own remediation modules. TruRisk Eliminate 2.0, released in October 2026, adds patch reliability scores, rollouts in waves with failure analysis, and compensating controls.
- Enterprise TruRisk Management (ETM): the risk platform that pulls Qualys and third-party findings into one view. Since 2025 it has added agentic AI "risk agents" and a Cyber Risk Assistant.
- Other modules: Policy Compliance, Web Application Scanning (WAS), CyberSecurity Asset Management (CSAM) and cloud security.
Tenable
- Nessus: the scanner. Essentials is free but limited, Professional is the paid single-scanner product, and Expert adds external attack surface and cloud infrastructure scanning.
- Tenable Vulnerability Management: the cloud platform, formerly http://Tenable.io . Tenable's buy page now lists it under the Tenable One brand.
- Tenable Security Center: the on-prem platform, formerly http://Tenable.sc .
- Tenable One: the exposure management platform covering cloud, identity, web apps, OT and, since 2026, AI tools (Tenable AI Exposure). Tenable Hexa AI is its agentic AI engine.
- Tenable Patch Management: a patching add-on built on Adaptiva (since December 2024). Remediation workflows come from Vulcan Cyber, acquired in February 2025.
Qualys vs Tenable: features compared
Asset discovery and scanning
This is where both vendors are strongest, and the gap between them is small.
- Tenable: Nessus has one of the largest vulnerability check libraries in the industry. It handles credentialed and non-credentialed scans across operating systems, network devices, databases, virtualisation platforms and web servers. Tenable One extends discovery to OT, Active Directory and cloud.
- Qualys: VMDR combines the Cloud Agent, which assesses continuously with no scan windows, with network scanners for devices that can't run an agent. CSAM keeps a live asset inventory, including end-of-life and unauthorised software.
Edge: Tenable, narrowly, for breadth across OT and identity. Qualys's always-on agent is the more convenient model for distributed and remote endpoints.
Prioritisation
Both go beyond CVSS. Qualys's TruRisk score combines exploitability, threat intelligence and asset criticality. Tenable's Vulnerability Priority Rating (VPR) weighs threat intelligence and the likelihood of exploitation, and Tenable One adds an exposure score across the attack surface. Both now add agentic AI on top: Qualys's risk agents in ETM, and Tenable Hexa AI.
Edge: tie. Choose based on which score your team finds easier to act on.
Remediation: native vs bolted on
This is the biggest difference between the two.
- Qualys: native, but sold separately. Qualys built its own patching (Patch Management) and mitigation (TruRisk Eliminate) on the same Cloud Agent. Eliminate 2.0 (October 2026) adds patch reliability scoring, rollouts in waves with failure analysis and rollback guidance, and compensating controls. Some of those controls are applied through security tools you already run.
- Tenable: bolted on. Tenable Patch Management is an add-on built on Adaptiva's technology, and its remediation workflows came from the Vulcan Cyber acquisition. Through 2026 it has added phased rollouts and automatic Nessus agent rescans after patching. Tenable can create Jira and ServiceNow tickets, but it has no native way to apply a scripted fix or block a vulnerable application when no patch exists.
Edge: Qualys. Neither includes remediation in its core vulnerability management licence.
Compliance auditing
Both audit configurations against CIS benchmarks and regulatory frameworks such as PCI DSS, HIPAA and NIST.
- Qualys: this is a separate module, Policy Compliance, running on the same agent and scanners as VMDR.
- Tenable: compliance audits are built into Nessus Professional and Expert, Tenable Vulnerability Management and Tenable Security Center.
For on-prem and cloud auditing, Tenable Security Center is the stronger fit if you need everything on-premises. Qualys suits teams happy with a SaaS platform.
Edge: tie. Tenable bundles compliance more simply; Qualys's module is deeper but costs extra.
Cloud, containers and web apps
Both cover cloud workloads, containers and web applications, but through separate products or modules.
- Qualys: Web Application Scanning (WAS) and its cloud security apps.
- Tenable: Tenable Web App Scanning, Tenable Cloud Security, and container scanning in Tenable Vulnerability Management.
Edge: tie. Budget for the extra licences either way.
Deployment
- Qualys: SaaS-first, with a private cloud platform for organisations that need it.
- Tenable: SaaS (Tenable Vulnerability Management) or fully on-prem (Tenable Security Center). Standalone Nessus scanners can run anywhere, including air-gapped networks.
Edge: Tenable, for organisations that need on-prem or offline options.
Qualys vs Nessus
This isn't quite a like-for-like comparison. Nessus is a scanner. Qualys VMDR is a full vulnerability management platform with asset inventory, prioritisation, dashboards and optional remediation. The fairer comparisons are:
- Nessus Professional vs Qualys VMDR: for a small team that mainly needs scanning, Nessus Professional ($4,790 a year, unlimited IPs on one scanner) is simpler and has a published price.
- Tenable Vulnerability Management vs Qualys VMDR: the platform-to-platform comparison for most organisations.
Qualys vs Tenable pricing in 2026
Tenable publishes list prices for its entry products. Qualys doesn't publish prices; every deal is quoted on asset count, modules and contract length.
What this means in practice
- For small teams, Tenable is easier to buy: Nessus Professional or a 100-asset Tenable Vulnerability Management subscription can go on a card.
- For enterprises, both end up quote-based, and multi-year terms and asset volume move the price more than list rates do.
- Remediation is extra with both. Budget for Qualys Patch Management or TruRisk Eliminate, or Tenable Patch Management, on top of the vulnerability management licence. Otherwise compare against platforms that include remediation natively.
Prices change often. Confirm current pricing with each vendor before you buy.
Where each falls short
Qualys
- The full stack is modular. VMDR, Patch Management, TruRisk Eliminate, Policy Compliance and WAS are licensed separately, so total cost is hard to estimate before a quote.
- No published pricing, which slows down evaluation for smaller teams.
- Many apps inside one platform. Powerful, but it takes time to learn and configure well.
- Some patchless mitigation relies on your other tools. Eliminate 2.0 applies part of its compensating controls through the security tools you already run.
Tenable
- Remediation is bolted on. Patching comes from an Adaptiva-based add-on, and workflows from the Vulcan Cyber acquisition, rather than from Tenable's own engine.
- No native fix when there's no patch. Tenable can prioritise and ticket a zero-day, but it can't apply a scripted mitigation or block the vulnerable software.
- The free tier has shrunk. Nessus Essentials is now a 30-day, 5-IP evaluation licence.
- Product sprawl. Nessus, Vulnerability Management, Security Center, Tenable One and its add-ons overlap, so it pays to be clear about which one you're buying.
When neither is enough
Qualys and Tenable both lead at finding vulnerabilities. If your backlog is growing because fixes don't keep up, a remediation-first platform may matter more than a better scanner.
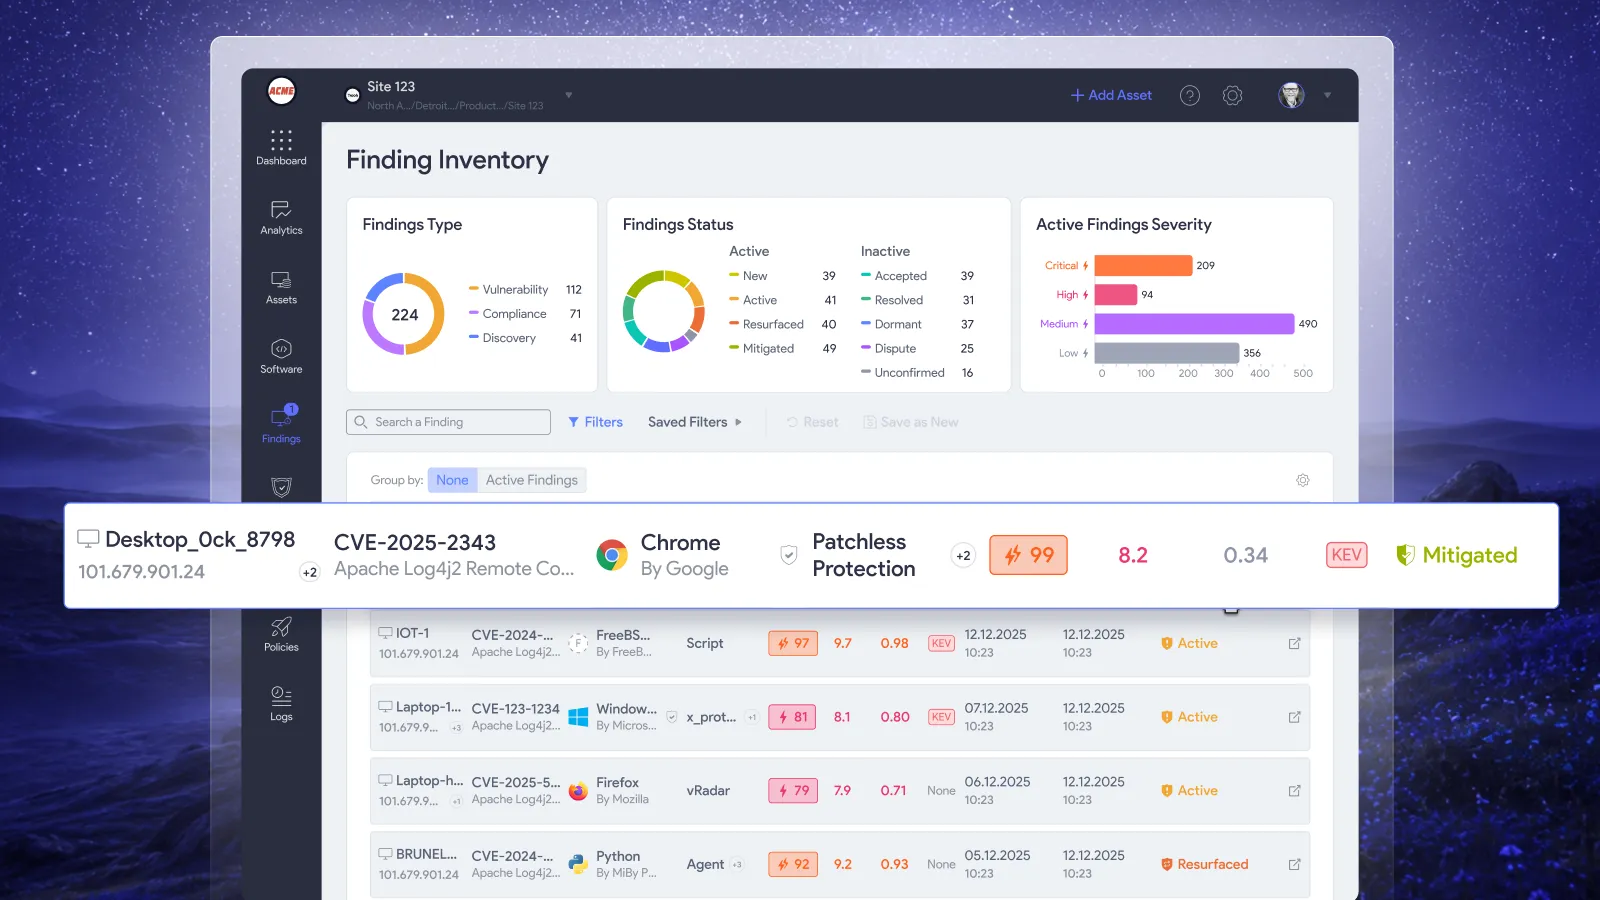
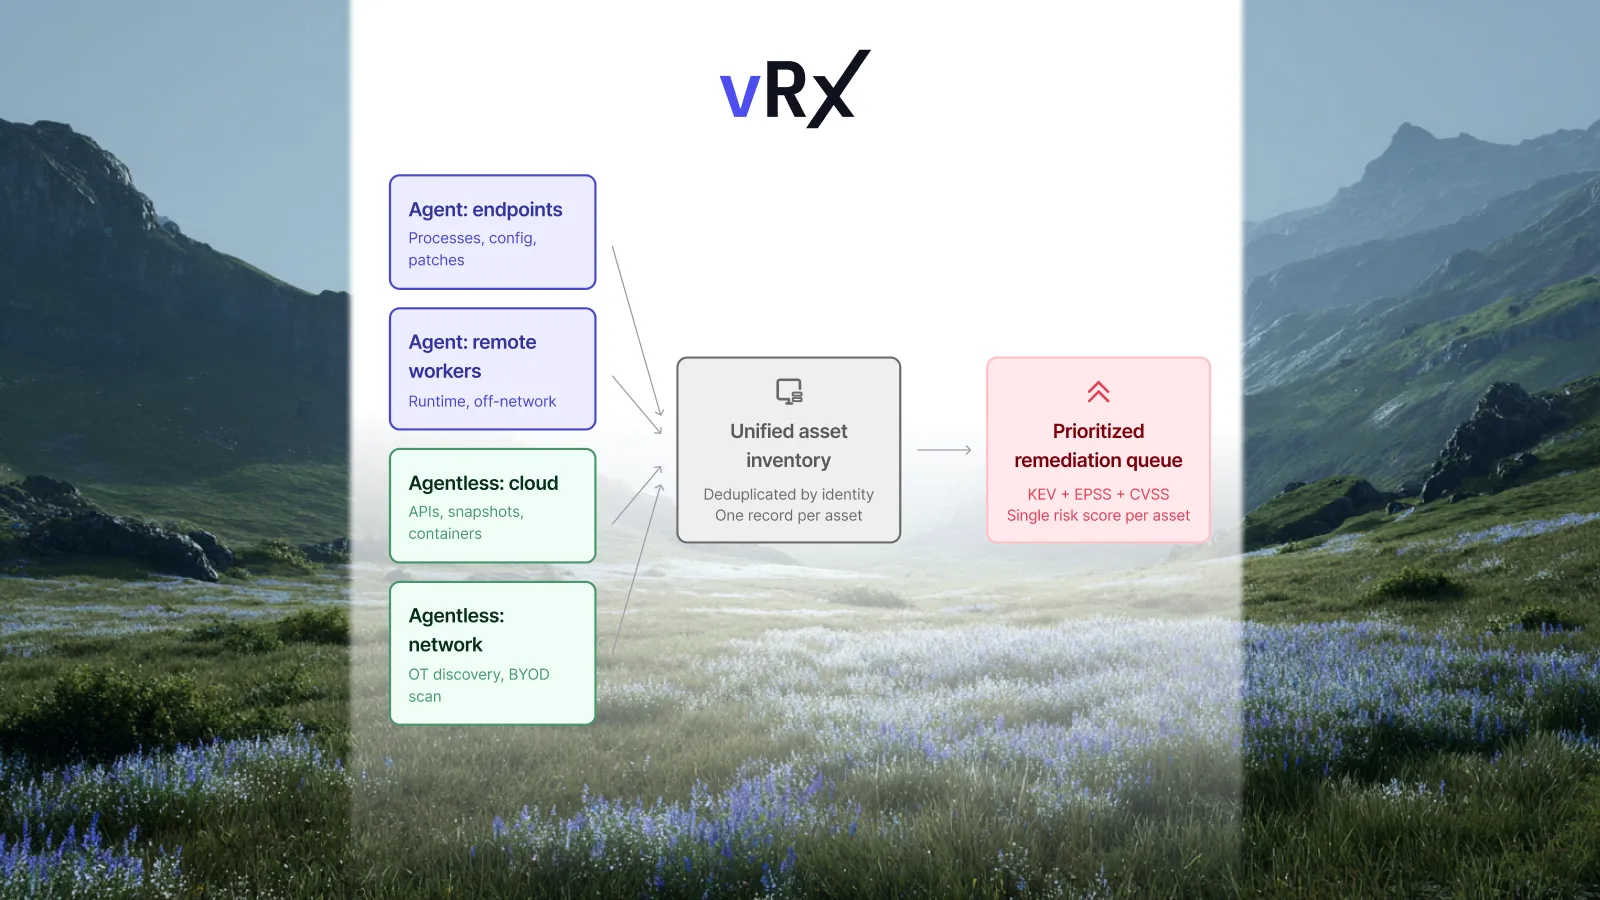
Vicarius vRx is SaaS. It finds vulnerabilities with an agent and the agentless vRadar scanner, which also covers web apps for the OWASP Top 10. It then fixes them natively through:
- Patching for Windows, macOS, Linux and 20,000+ third-party apps
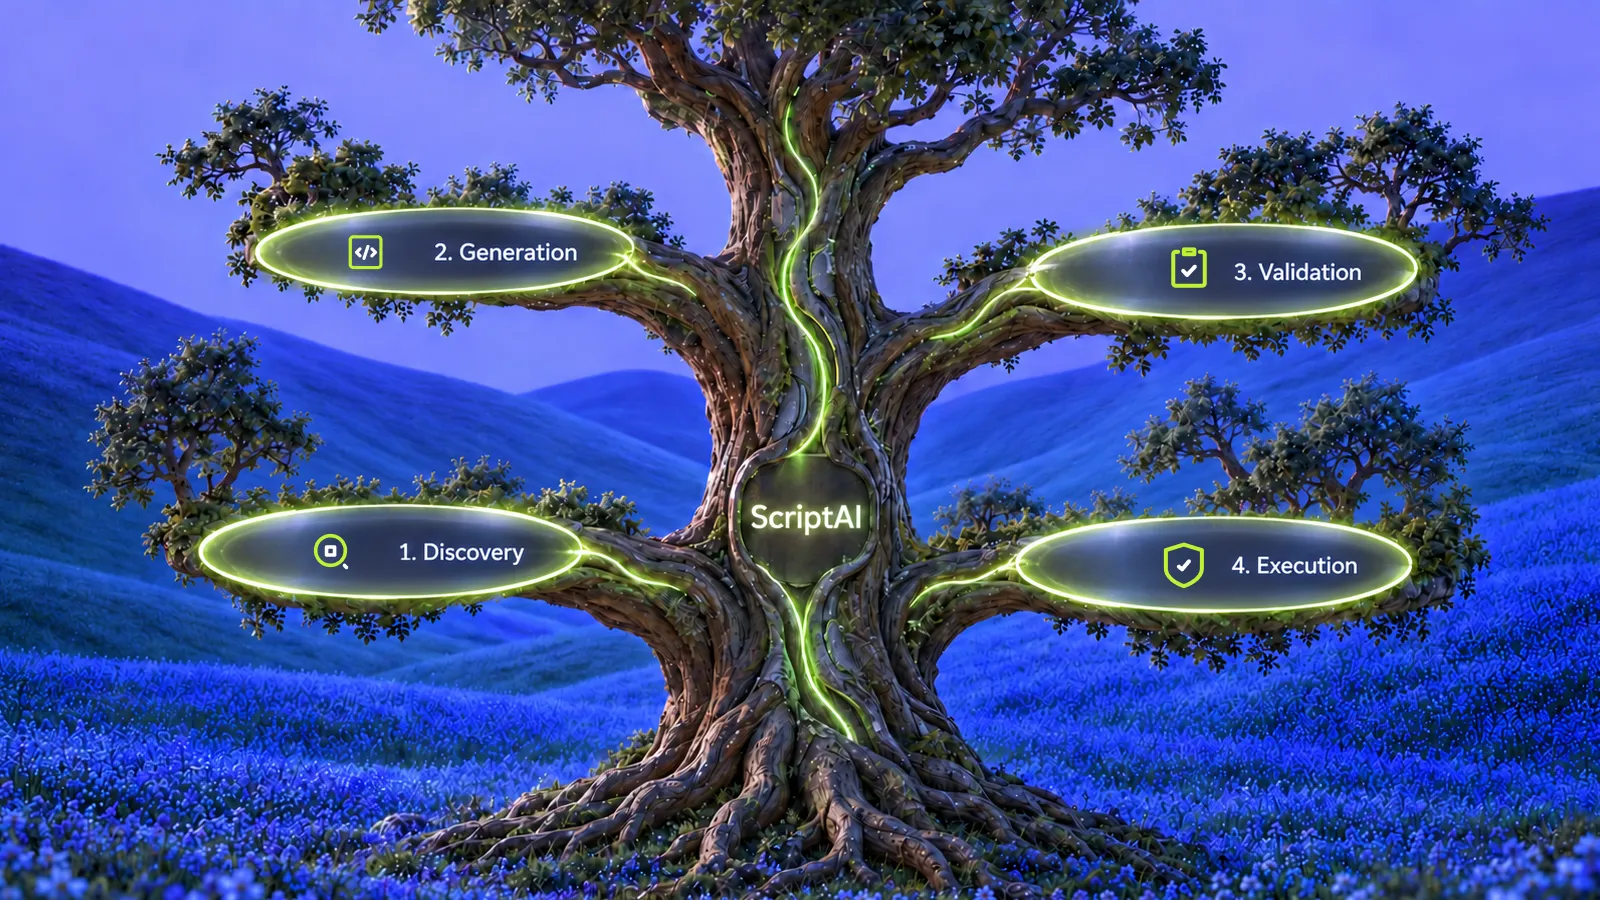
- vScript and ScriptAI scripted fixes
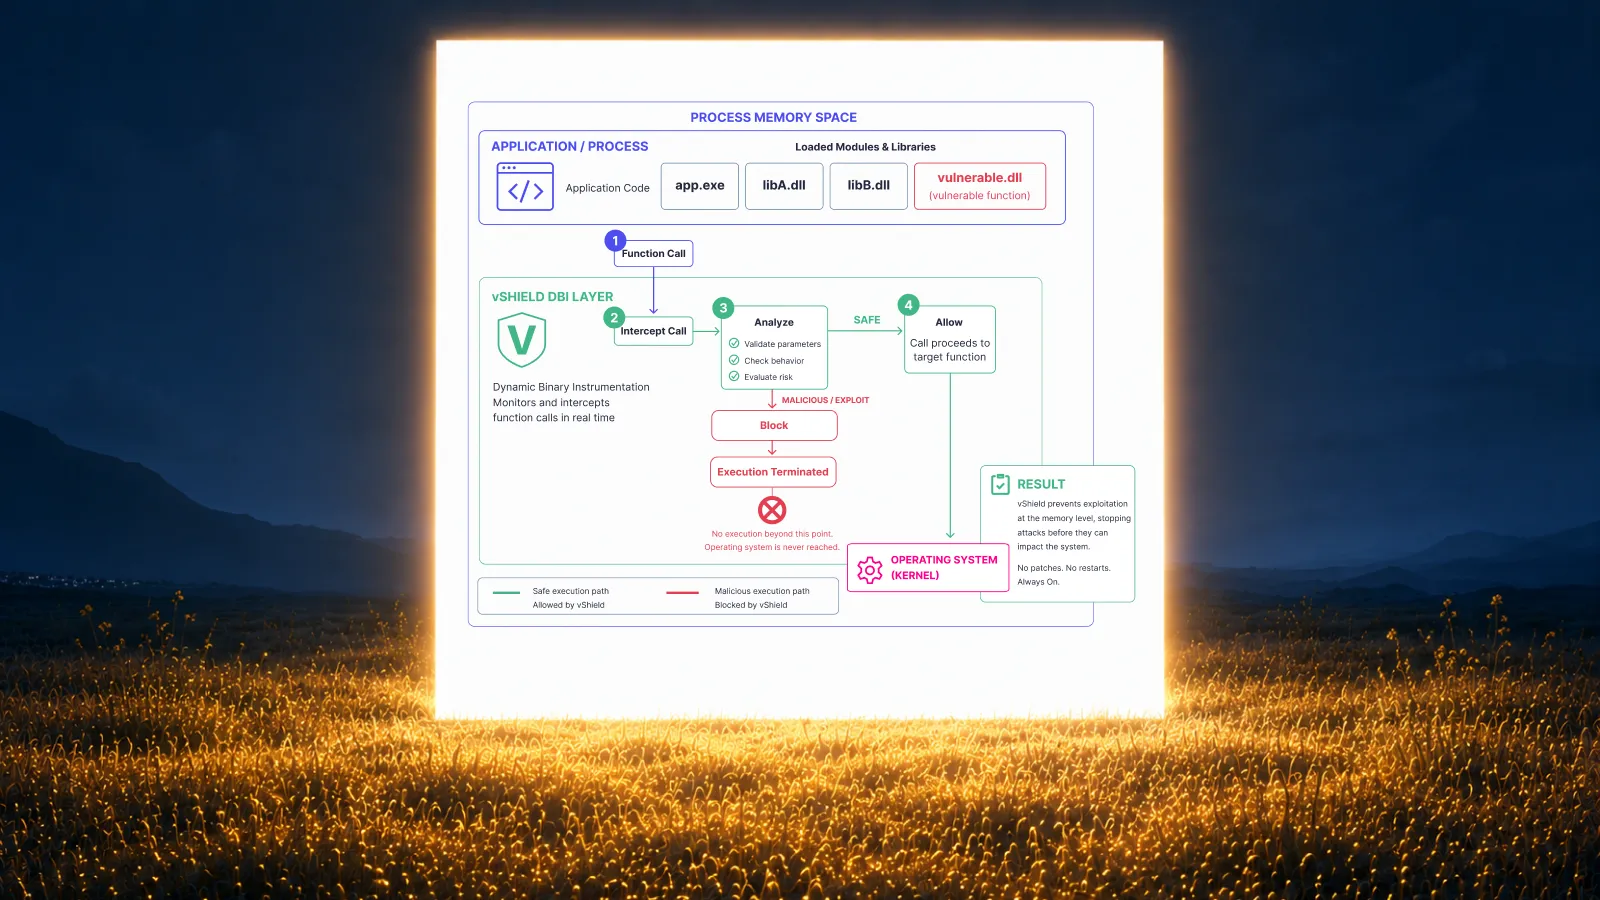
- vShield patchless protection for software you can't patch
It can also work alongside an existing Qualys or Tenable deployment.
What about Rapid7?
Rapid7 InsightVM / Exposure Command is the third of the traditional "big three". Its patching, Active Patching, is powered by Automox, so like Tenable's it is bolted on. See Qualys vs Rapid7 and Rapid7 vs Tenable. For a wider list, see Top Tenable Alternatives in 2026.
Frequently asked questions
Is Qualys better than Tenable?
Neither is better across the board. Tenable has the edge on scanning breadth, on-prem deployment and transparent pricing. Qualys has the edge on remediation, because its patching and mitigation are its own, though they're licensed separately. Most teams decide based on deployment needs and how they plan to fix what they find.
What is the difference between Qualys and Nessus?
Nessus is Tenable's vulnerability scanner. Qualys VMDR is a cloud vulnerability management platform with asset inventory, TruRisk prioritisation and optional patching. The closest Tenable equivalent to Qualys VMDR is Tenable Vulnerability Management, which uses Nessus scanners and agents.
How much do Qualys and Tenable cost in 2026?
Tenable lists Nessus Professional at $4,790 a year and Nessus Expert at $6,790 a year. Tenable Vulnerability Management is listed at about $3,500–$3,700 a year for 100 assets. Qualys doesn't publish prices. Independent estimates put Qualys VMDR at roughly $199–$250 per asset per year, with patching and compliance modules extra.
Which is better for compliance auditing across on-prem and cloud?
Both audit against CIS benchmarks and frameworks such as PCI DSS and HIPAA. Tenable Security Center suits organisations that need auditing to run fully on-premises. Qualys Policy Compliance suits teams that prefer a single SaaS platform covering on-prem and cloud assets through its agent and scanners.
Can Qualys or Tenable patch vulnerabilities?
Yes, but only with add-ons. Qualys Patch Management and TruRisk Eliminate are Qualys's own technology. Tenable Patch Management is built on Adaptiva. Neither is included in the core vulnerability management licence.
Tenable vs Qualys vs Rapid7: which is best?
All three are strong at finding vulnerabilities. Tenable leads on scanning breadth, Qualys on native remediation, and Rapid7 on ties to its detection and response products. Rapid7's patching is powered by Automox. See Qualys vs Rapid7 and Rapid7 vs Tenable.
What are the best alternatives to Qualys and Tenable?
Rapid7, Microsoft Defender Vulnerability Management, ManageEngine Vulnerability Manager Plus, Greenbone OpenVAS (free), Automox and Vicarius vRx. vRx stands out if remediation is the priority, because patching, scripted fixes and patchless protection are all native. See Top Tenable Alternatives in 2026.
Sources
- Tenable: Buy Tenable products (list prices) (checked October 2026)
- Tenable: Nessus Essentials
- Tenable: Tenable Patch Management 2026 release notes (October 2026)
- Adaptiva: Tenable Patch Management
- Tenable: Tenable Completes Acquisition of Vulcan Cyber (February 2025)
- Tenable: Tenable Advances Exposure Management with Coverage Across Every Major AI Platform (August 2026)
- Qualys: Qualys Unveils TruRisk Eliminate 2.0 with TruConfidence (October 2026)
- Qualys: Agentic AI in Enterprise TruRisk Management
- Qualys: Community Edition
- Ciphers Security: Qualys Pricing Explained: VMDR, WAS & Patch Costs (2026) (independent estimate)