Last updated: October 2026
Rapid7 vs Tenable: the quick verdict
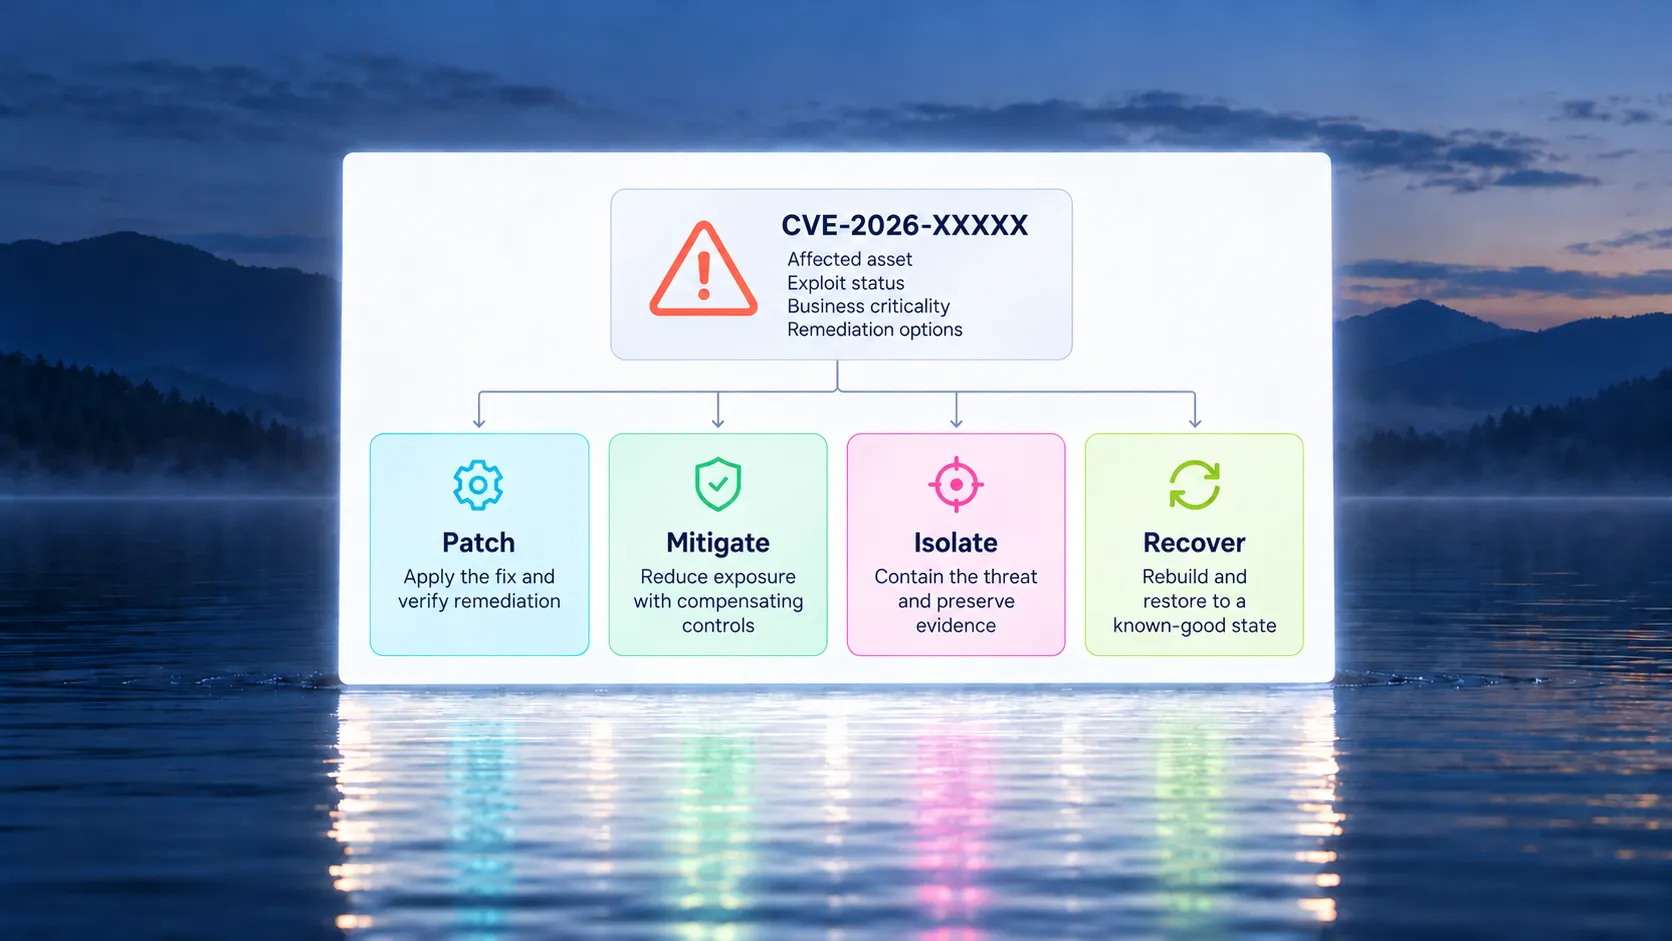
Choose Tenable if scanning depth matters most, if you need fully on-prem or air-gapped options, or if you want published prices. Choose Rapid7 if you already use Rapid7 for detection and response, or if you want remediation tracking and patching inside the same Exposure Command platform. Both are excellent scanners. Both deliver patching through a partner, not their own engine.
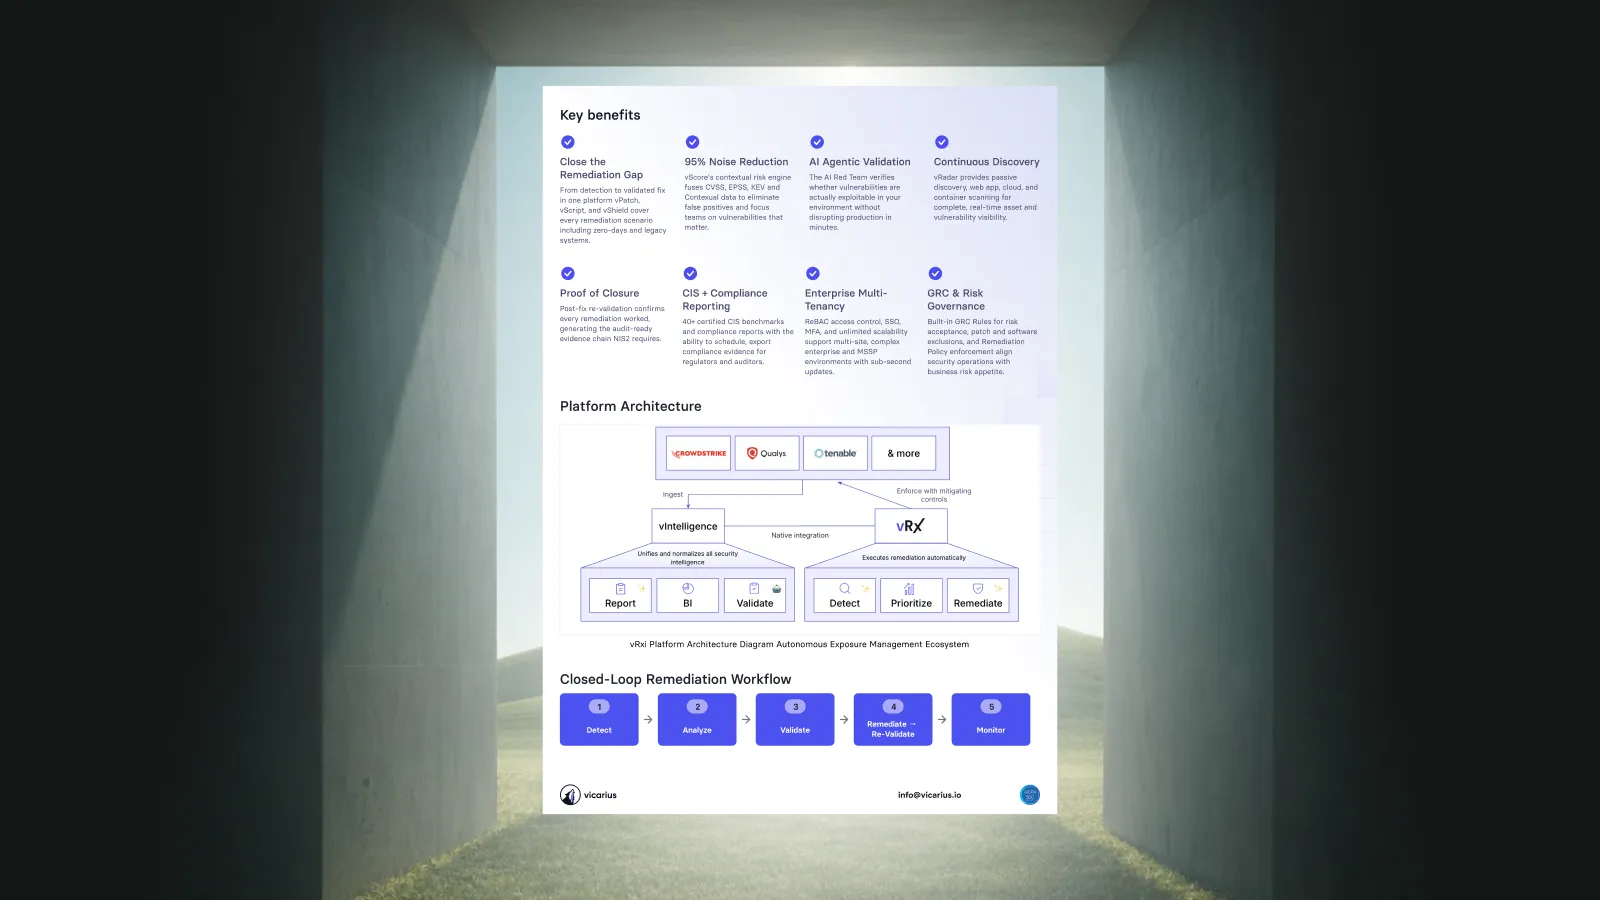
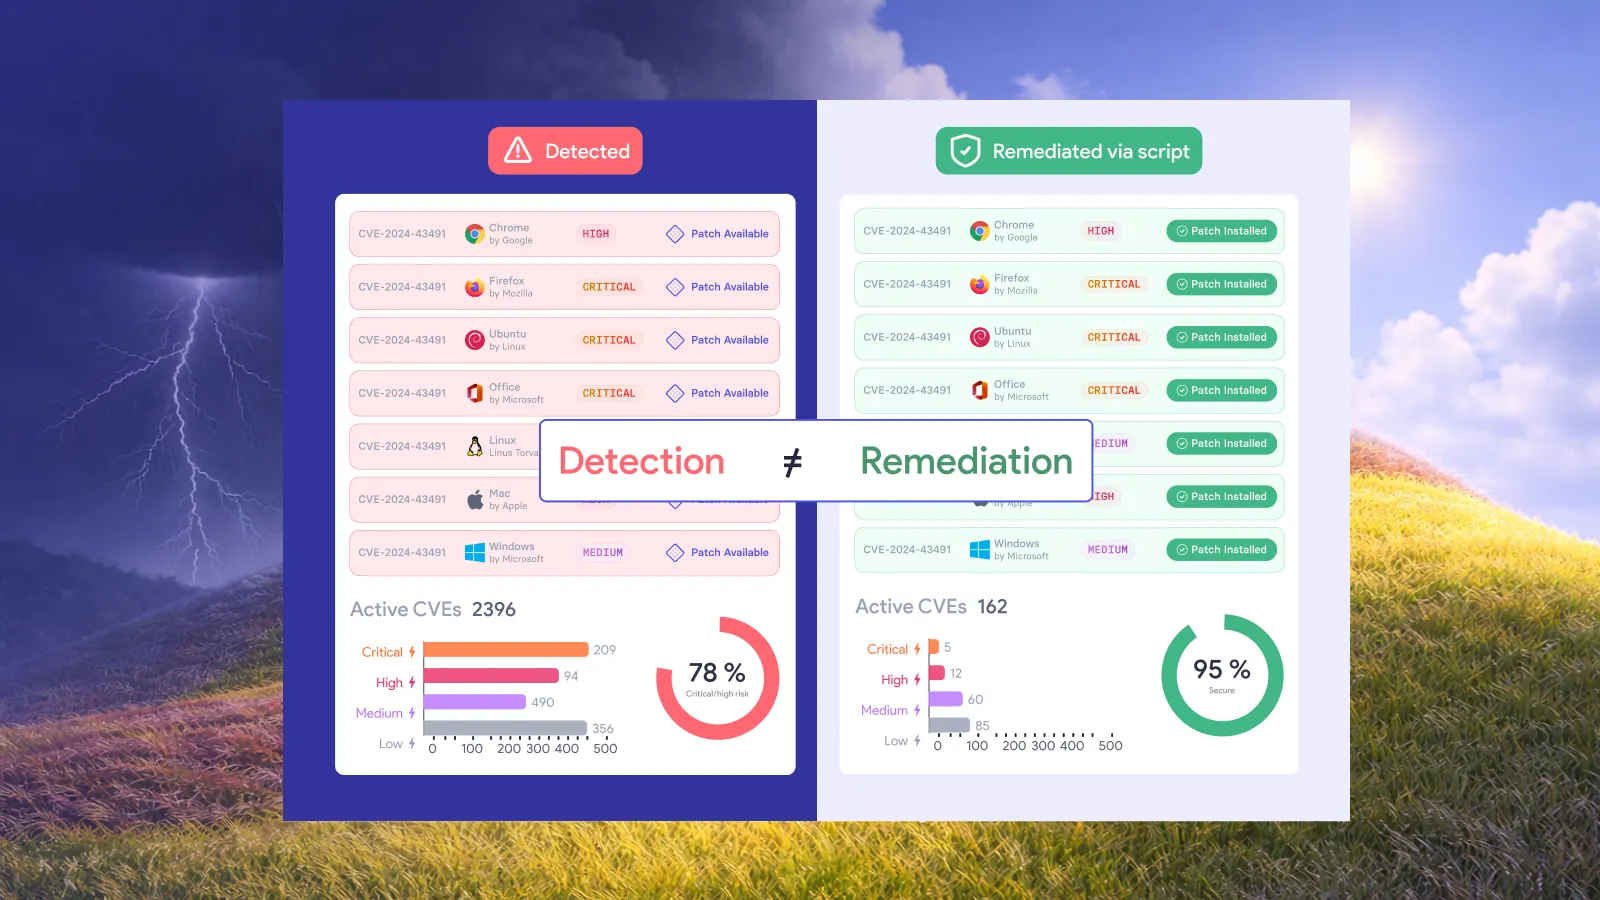
If your real bottleneck is fixing, not finding, a remediation-first platform such as Vicarius vRx includes patching, scripted fixes and patchless protection natively, rather than through a partner.
Disclosure: Vicarius makes vRx, a vulnerability remediation platform. We've aimed to be fair to both Rapid7 and Tenable.
Rapid7 and Tenable in 2026: what each sells
Both vendors have moved from standalone scanners to exposure management platforms, so older comparisons that set "Nexpose, InsightVM, http://Tenable.io and http://Tenable.sc " side by side are now out of date.
Rapid7
- InsightVM: Rapid7's vulnerability management product. It combines an on-prem Security Console and scan engines with the cloud-based Insight Agent and live dashboards.
- Nexpose: the older, fully on-prem version of InsightVM. It's still supported for organisations that can't use the cloud.
- Exposure Command: Rapid7's exposure management platform, sold as Essentials (InsightVM plus attack surface management) and Ultimate (adding cloud and application security). It includes Remediation Hub, which added AI-generated risk summaries in late 2025.
- Active Patching, powered by Automox: patching and virtual patching for Exposure Command, launched in July 2025.
- Surface Command: external attack surface discovery.
Tenable
- Nessus: the scanner. Essentials is free but limited, Professional is the paid single-scanner product, and Expert adds web app scanning and external attack surface discovery.
- Tenable Vulnerability Management: the cloud platform, formerly http://Tenable.io . Tenable's buy page now lists it under the Tenable One brand.
- Tenable Security Center: the on-prem platform, formerly http://Tenable.sc .
- Tenable One: the exposure management platform covering cloud, identity, web apps, OT and, since 2026, AI tools (Tenable AI Exposure). Tenable Hexa AI is its agentic AI engine.
- Tenable Patch Management: a patching add-on built on Adaptiva (since December 2024). Remediation workflows come from Vulcan Cyber, acquired in February 2025.
Rapid7 vs Tenable: features compared
Asset discovery and scanning
- Tenable: Nessus has one of the largest vulnerability check libraries in the industry. It handles credentialed and non-credentialed scans across operating systems, network devices, databases, virtualisation and web servers. Tenable One extends discovery to OT, Active Directory and cloud.
- Rapid7: InsightVM pairs scan engines with the Insight Agent for continuous endpoint assessment. Exposure Command and Surface Command add cloud and external attack surface discovery.
Edge: Tenable, for breadth and depth of checks, especially in OT and identity.
Prioritisation
Rapid7's Active Risk score weighs exploitability and threat intelligence, and Remediation Hub now adds AI-generated risk summaries that use CISA KEV and EPSS data. Tenable's Vulnerability Priority Rating (VPR) weighs threat intelligence and the likelihood of exploitation. Tenable One adds an exposure score and Hexa AI agents on top.
Edge: tie. Both are well beyond plain CVSS.
Remediation: native vs bolted on
The two are more alike here than their marketing suggests.
- Rapid7: bolted on. Active Patching for Exposure Command (July 2025) is powered by Automox's engine. It patches Windows, macOS, Linux and third-party apps, and can apply virtual patches or compensating controls when no patch exists. Rapid7's own strength is tracking: Remediation Hub, Remediation Projects and IT-ready tickets. InsightVM-only customers still remediate through tickets and other tools.
- Tenable: bolted on. Tenable Patch Management is an add-on built on Adaptiva. Through 2026 it has added phased rollouts and automatic Nessus agent rescans after patching. Remediation workflows come from Vulcan Cyber. Tenable has no way to apply a scripted fix or a virtual patch when no patch exists.
Edge: Rapid7, for patchless mitigation and remediation tracking. Neither builds its own patching engine.
Compliance auditing
Both audit configurations against CIS benchmarks and frameworks such as PCI DSS and DISA STIG.
- Rapid7: policy assessment in InsightVM.
- Tenable: compliance audits in Nessus Professional and Expert, Tenable Vulnerability Management and Tenable Security Center.
Edge: tie.
Cloud, containers and web apps
- Rapid7: Exposure Command Ultimate adds cloud security, including cloud runtime security and data security posture management (DSPM) in 2026, plus application security.
- Tenable: sells Tenable Cloud Security and Tenable Web App Scanning separately or within Tenable One.
Edge: tie. Both charge extra for these.
Deployment
- Rapid7: InsightVM uses an on-prem Security Console and scan engines alongside the cloud platform. Nexpose is the fully on-prem option.
- Tenable: offers a pure SaaS route (Tenable Vulnerability Management), a fully on-prem route (Tenable Security Center), and standalone Nessus scanners that work in air-gapped networks.
Edge: Tenable, narrowly.
InsightVM vs Nessus (and Nexpose vs Nessus)
These aren't quite like-for-like.
- Nessus is a scanner.
- InsightVM is a vulnerability management platform, with dashboards, Active Risk prioritisation and remediation tracking.
- Nexpose is InsightVM's on-prem predecessor.
The fair comparisons are:
- Nessus Professional vs Nexpose: both on-prem scanners. Nessus has the published price ($4,790 a year) and the larger check library. Nexpose adds more built-in management features.
- Tenable Vulnerability Management vs InsightVM: the platform-to-platform comparison most teams actually need. Tenable leads on scanning breadth, Rapid7 on remediation tracking and ties to its detection products.
Rapid7 vs Tenable pricing in 2026
Tenable publishes list prices for its entry products. Rapid7 no longer shows prices on its InsightVM pricing page; Exposure Command packages are quoted by the account team. Nessus is licensed per scanner; Tenable Vulnerability Management and InsightVM are licensed per asset, so their cost grows with your fleet.
What this means in practice
- For small teams, Tenable is easier to buy without talking to sales.
- Per asset, InsightVM estimates (about $19–$23 per asset per year) come in below Tenable Vulnerability Management's list price (about $35–$37 per asset per year at 100 assets). Volume and bundling change this a lot.
- Remediation is extra with both. Active Patching needs Exposure Command; Tenable Patch Management is a separate add-on. Budget for it, or compare against platforms that include remediation natively.
Prices change often. Confirm current pricing with each vendor before you buy.
Where each falls short
Rapid7
- Patching isn't Rapid7's own. Active Patching runs on Automox's engine and needs Exposure Command, so InsightVM-only customers still rely on tickets and separate tools.
- Platform transition. InsightVM, Nexpose, Exposure Command and Surface Command overlap, so it pays to be clear about which package you're buying.
- Hybrid infrastructure. InsightVM still needs an on-prem Security Console and scan engines alongside the cloud platform.
- No published pricing.
Tenable
- Patching isn't Tenable's own either. Tenable Patch Management is built on Adaptiva, and its workflows came from the Vulcan Cyber acquisition.
- No fix when there's no patch. Tenable can prioritise and ticket a zero-day, but it can't apply a scripted mitigation or a virtual patch.
- The free tier has shrunk. Nessus Essentials is now a 30-day, 5-IP evaluation licence.
- Product sprawl. Nessus, Vulnerability Management, Security Center, Tenable One and its add-ons overlap.
When neither is enough
Rapid7 and Tenable both lead at finding vulnerabilities, and both rely on partners to fix them. If your backlog is growing because fixes don't keep up, a platform with native remediation may matter more than a better scanner.
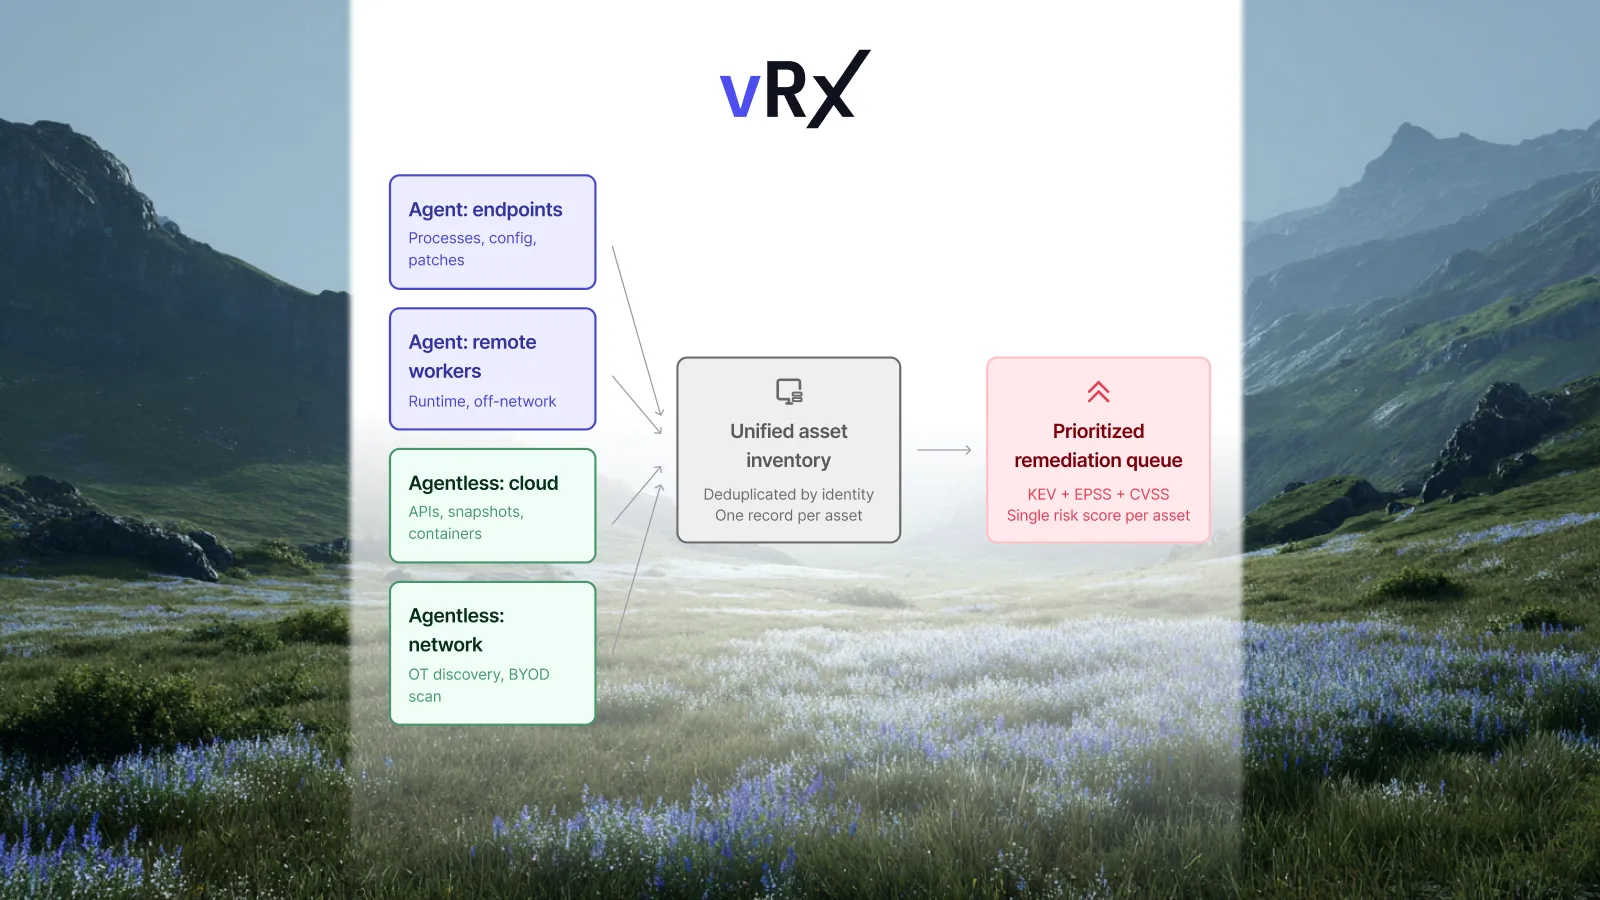
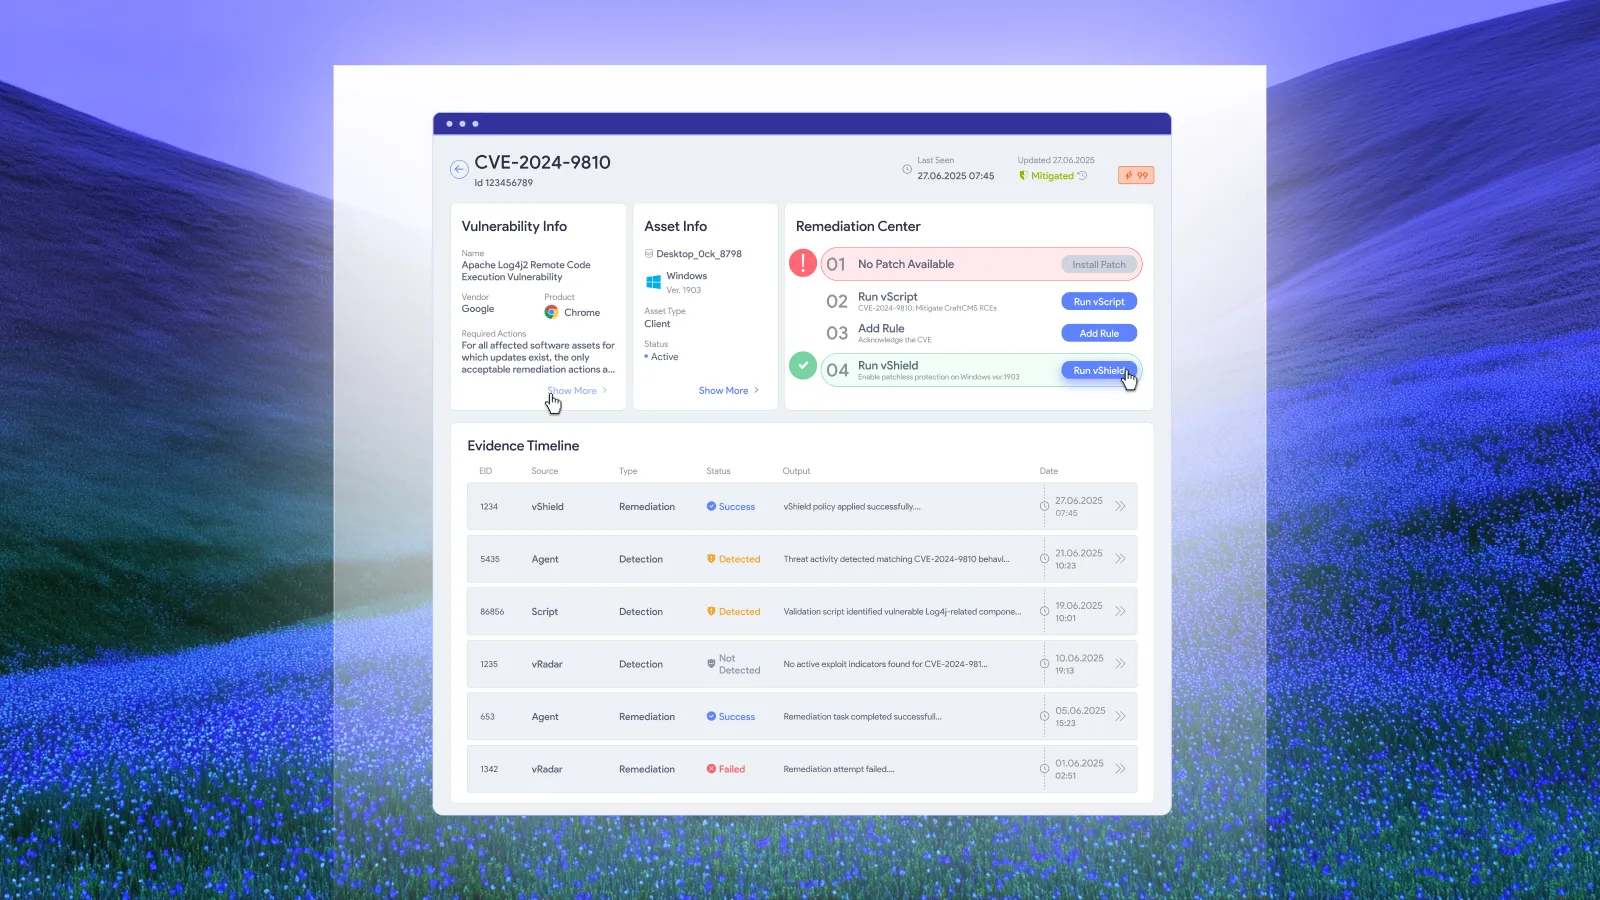
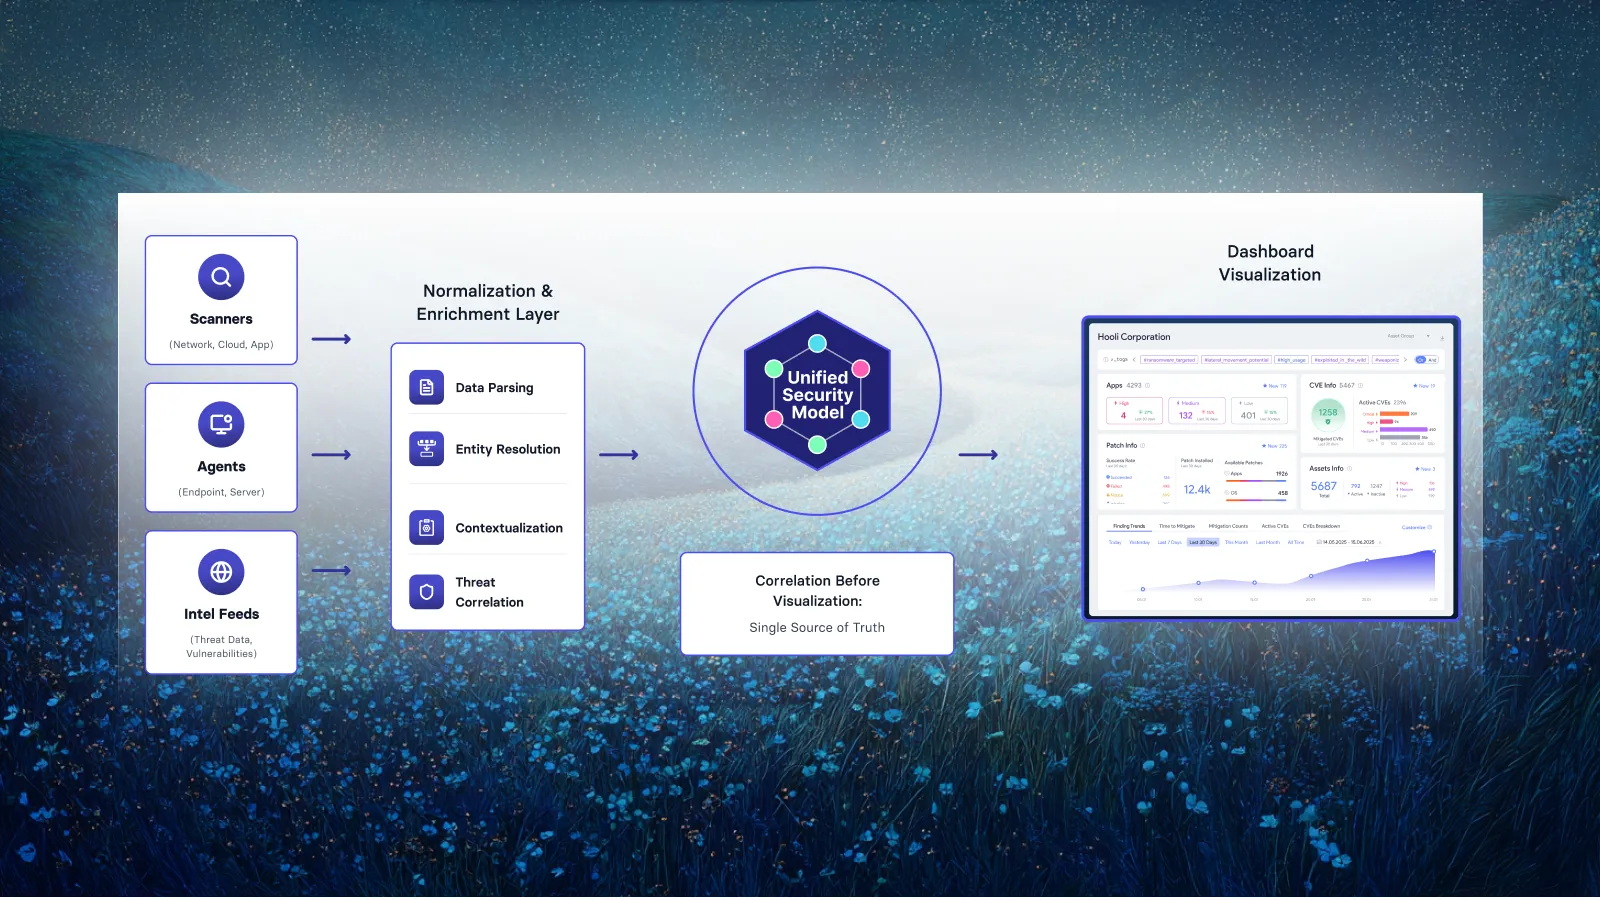
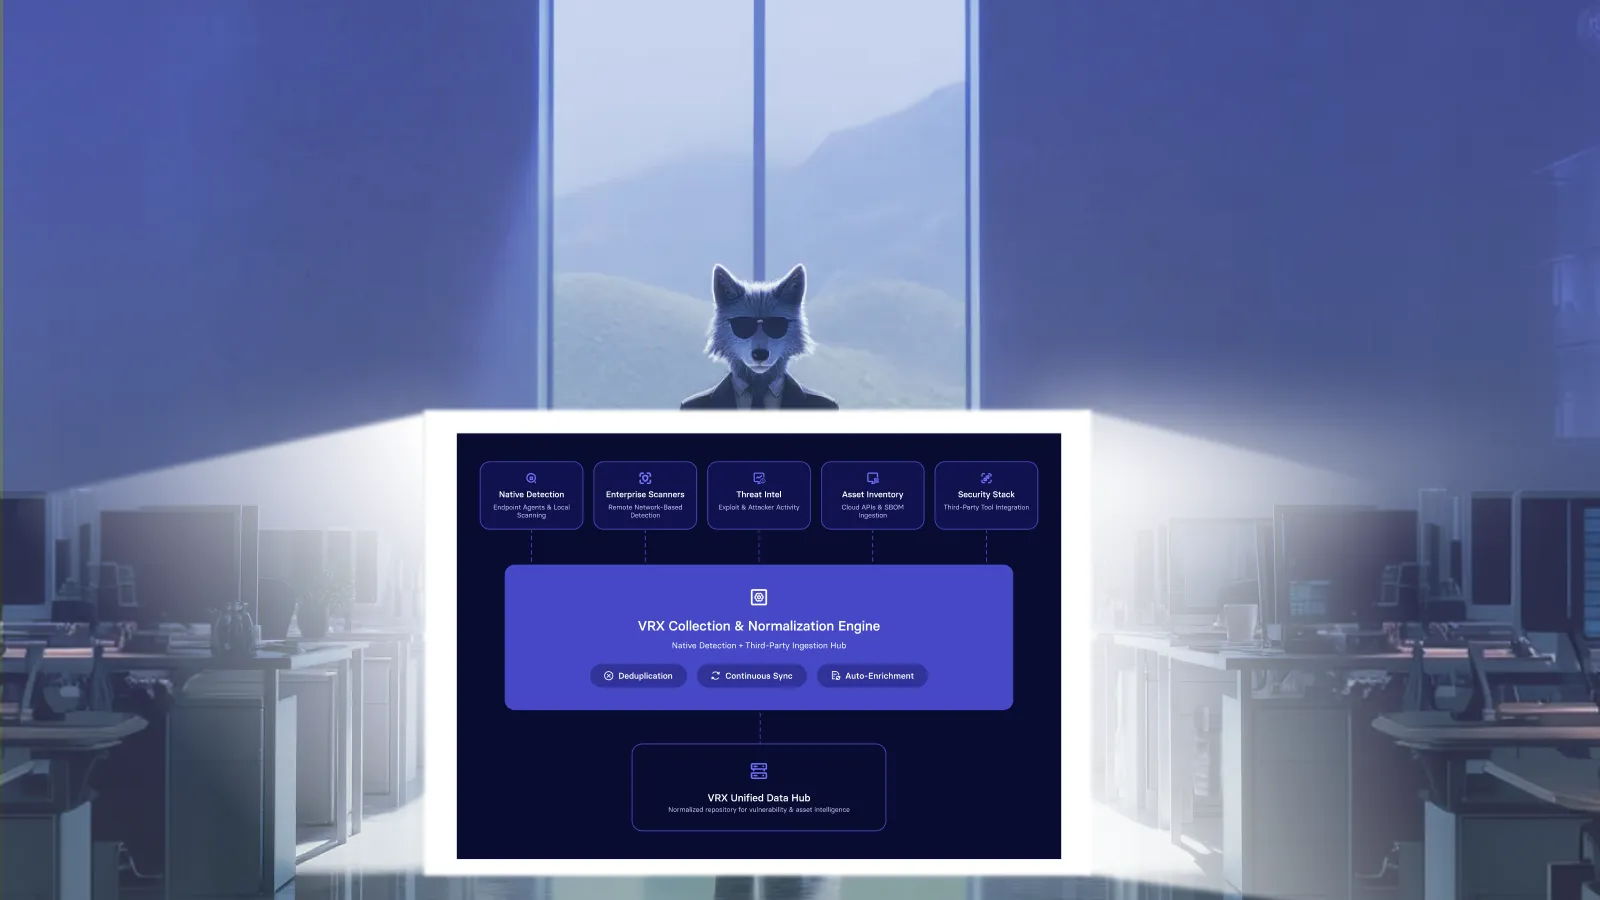
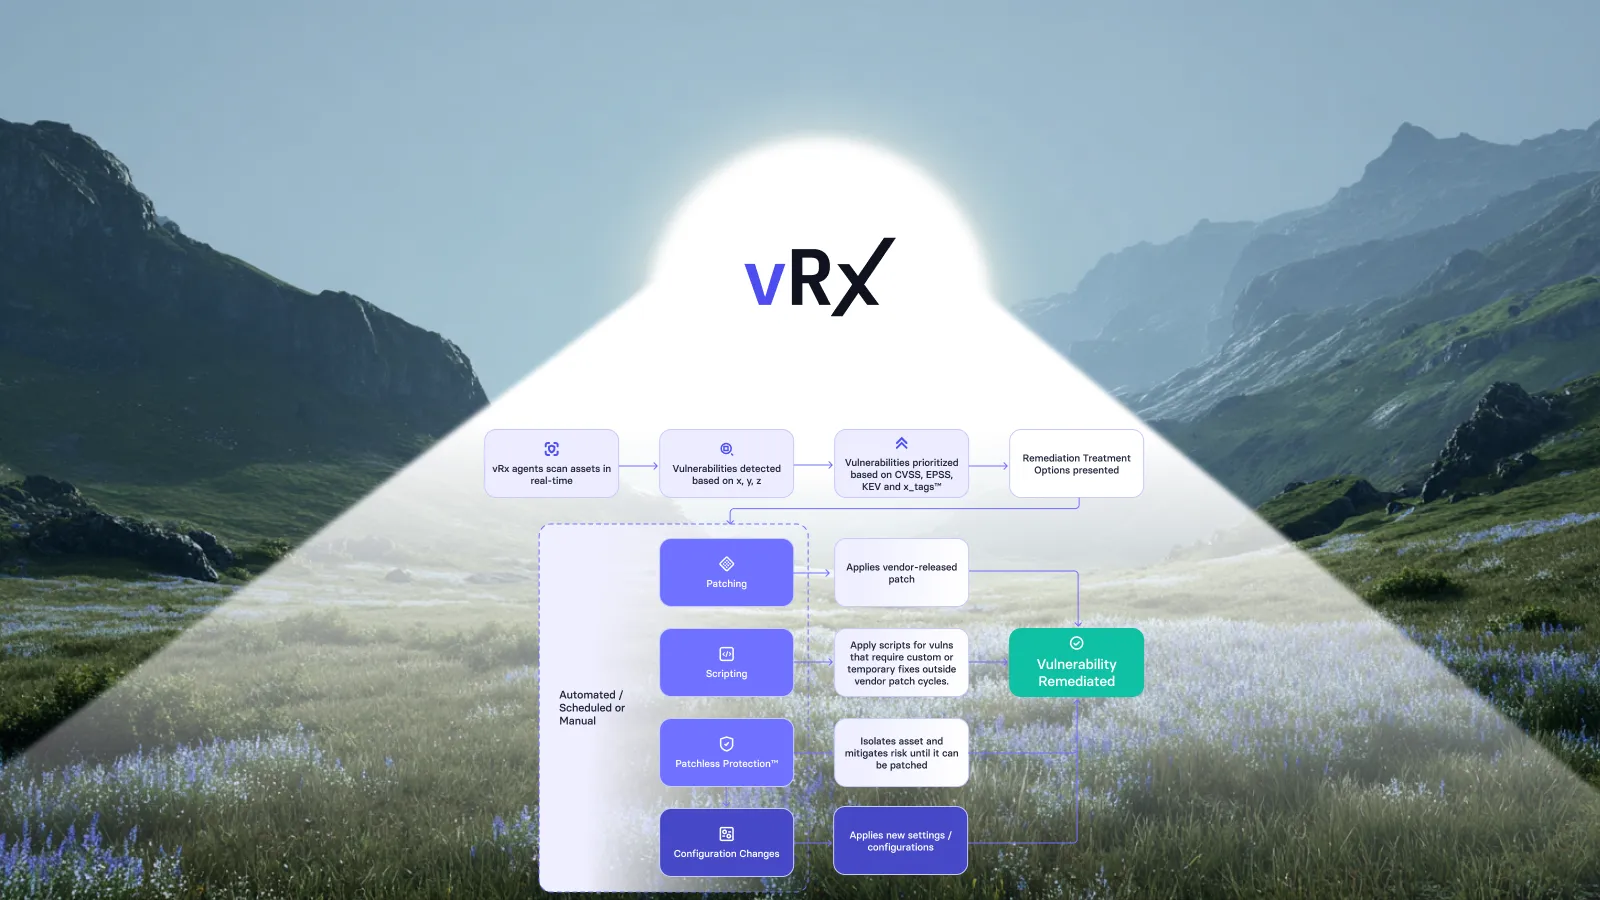
Vicarius vRx is SaaS. It finds vulnerabilities with an agent and the agentless vRadar scanner, which also covers web apps for the OWASP Top 10. It then fixes them natively through:
- Patching for Windows, macOS, Linux and 20,000+ third-party apps
- vScript and ScriptAI scripted fixes
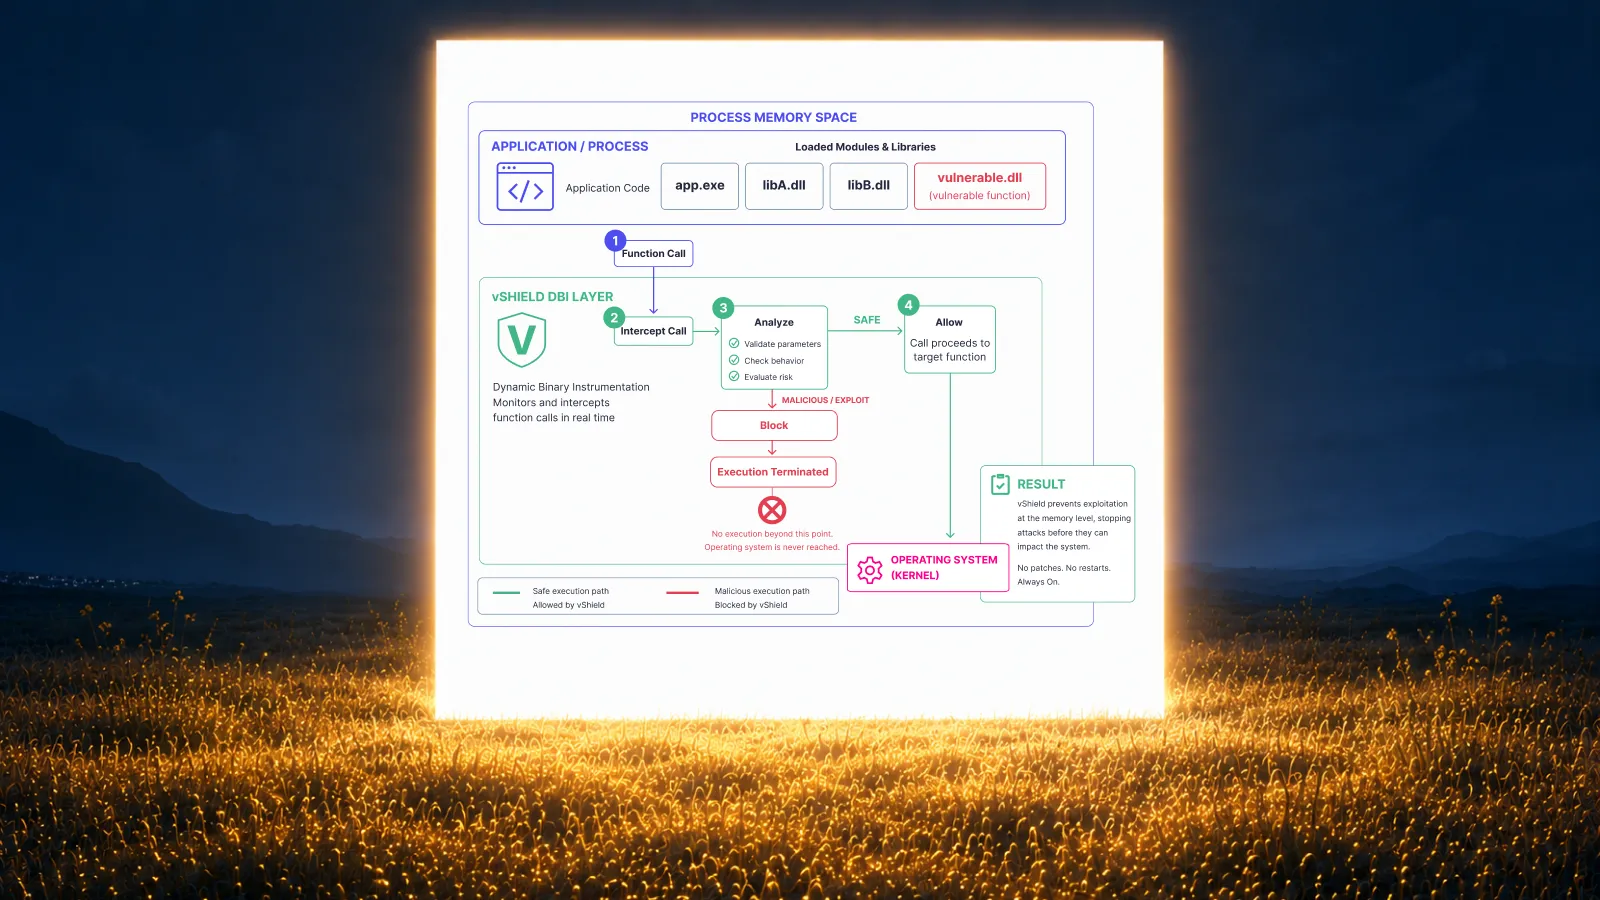
- vShield patchless protection for software you can't patch
It can also work alongside an existing Rapid7 or Tenable deployment.
What about Qualys?
Qualys VMDR is the third of the traditional "big three". Unlike Rapid7 and Tenable, its patching and mitigation (Patch Management and TruRisk Eliminate) are its own technology, though they're licensed separately. See Qualys vs Tenable and Qualys vs Rapid7. For a wider list, see Top Tenable Alternatives in 2026.
Frequently asked questions
Which is better: Rapid7 or Tenable?
Neither is better across the board. Tenable is stronger at scanning depth, OT and identity coverage, on-prem and air-gapped deployment, and transparent pricing. Rapid7 is stronger at remediation tracking, patchless mitigation through Active Patching, and integration with its own detection and response products. Both rely on partners for patching.
What is the difference between InsightVM and Nessus?
Nessus is Tenable's vulnerability scanner. InsightVM is Rapid7's vulnerability management platform, with scan engines, the Insight Agent, Active Risk prioritisation, dashboards and remediation tracking. The closest Tenable equivalent to InsightVM is Tenable Vulnerability Management, which uses Nessus scanners and agents.
Nexpose vs Nessus: which should I use?
Both are on-prem vulnerability scanners. Nessus Professional has a published price ($4,790 a year) and one of the largest check libraries. Nexpose, the on-prem version of Rapid7's InsightVM, adds more built-in management and reporting. Organisations moving to the cloud usually compare Tenable Vulnerability Management with InsightVM instead.
How much do Rapid7 and Tenable cost in 2026?
Tenable lists Nessus Professional at $4,790 a year and Nessus Expert at $6,790 a year, each per scanner licence and not tied to asset count. Tenable Vulnerability Management is priced per asset, at about $3,500–$3,700 a year for 100 assets. Rapid7 doesn't publish prices. Independent estimates put InsightVM at roughly $1.62–$1.93 per asset per month, with Exposure Command and Active Patching quoted separately.
Can Rapid7 or Tenable patch vulnerabilities?
Yes, but through partners. Rapid7's Active Patching is powered by Automox and is part of Exposure Command. Tenable Patch Management is built on Adaptiva and sold as an add-on. Neither vendor builds its own patching engine.
What are the best alternatives to Rapid7 and Tenable?
Qualys VMDR, Microsoft Defender Vulnerability Management, ManageEngine Vulnerability Manager Plus, Greenbone OpenVAS (free), Automox and Vicarius vRx. Qualys and vRx stand out for native remediation. See Top Tenable Alternatives in 2026.
Sources
- Tenable: Buy Tenable products (list prices) (checked October 2026)
- Tenable: Nessus Essentials
- Tenable: Tenable Patch Management 2026 release notes (October 2026)
- Adaptiva: Tenable Patch Management
- Tenable: Tenable Completes Acquisition of Vulcan Cyber (February 2025)
- Tenable: Tenable Advances Exposure Management with Coverage Across Every Major AI Platform (August 2026)
- Rapid7: Rapid7 Launches Active Patching Powered by Automox (July 2025)
- Rapid7: Rapid7 Accelerates Exposure Remediation with AI-Generated Risk Insights (October 2025)
- Rapid7: What's New in Rapid7 Products and Services: Q1 2026 (April 2026)
- Rapid7: InsightVM pricing and Exposure Command packages
- Costbench: Rapid7 InsightVM Pricing 2026 (independent estimate)